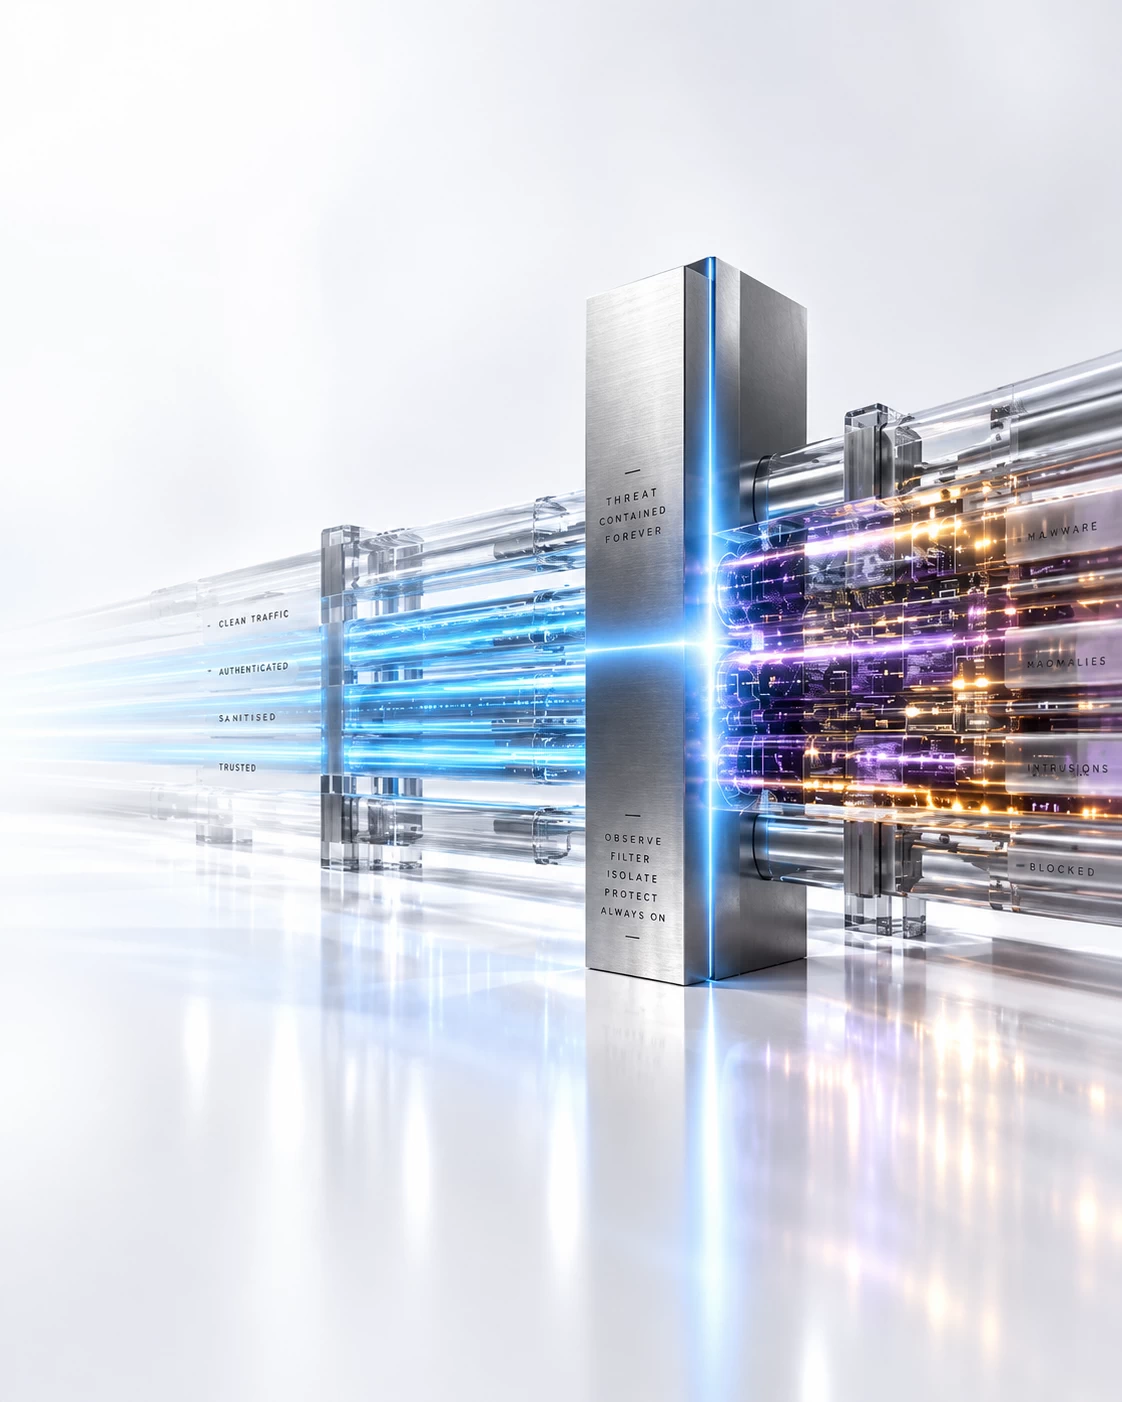
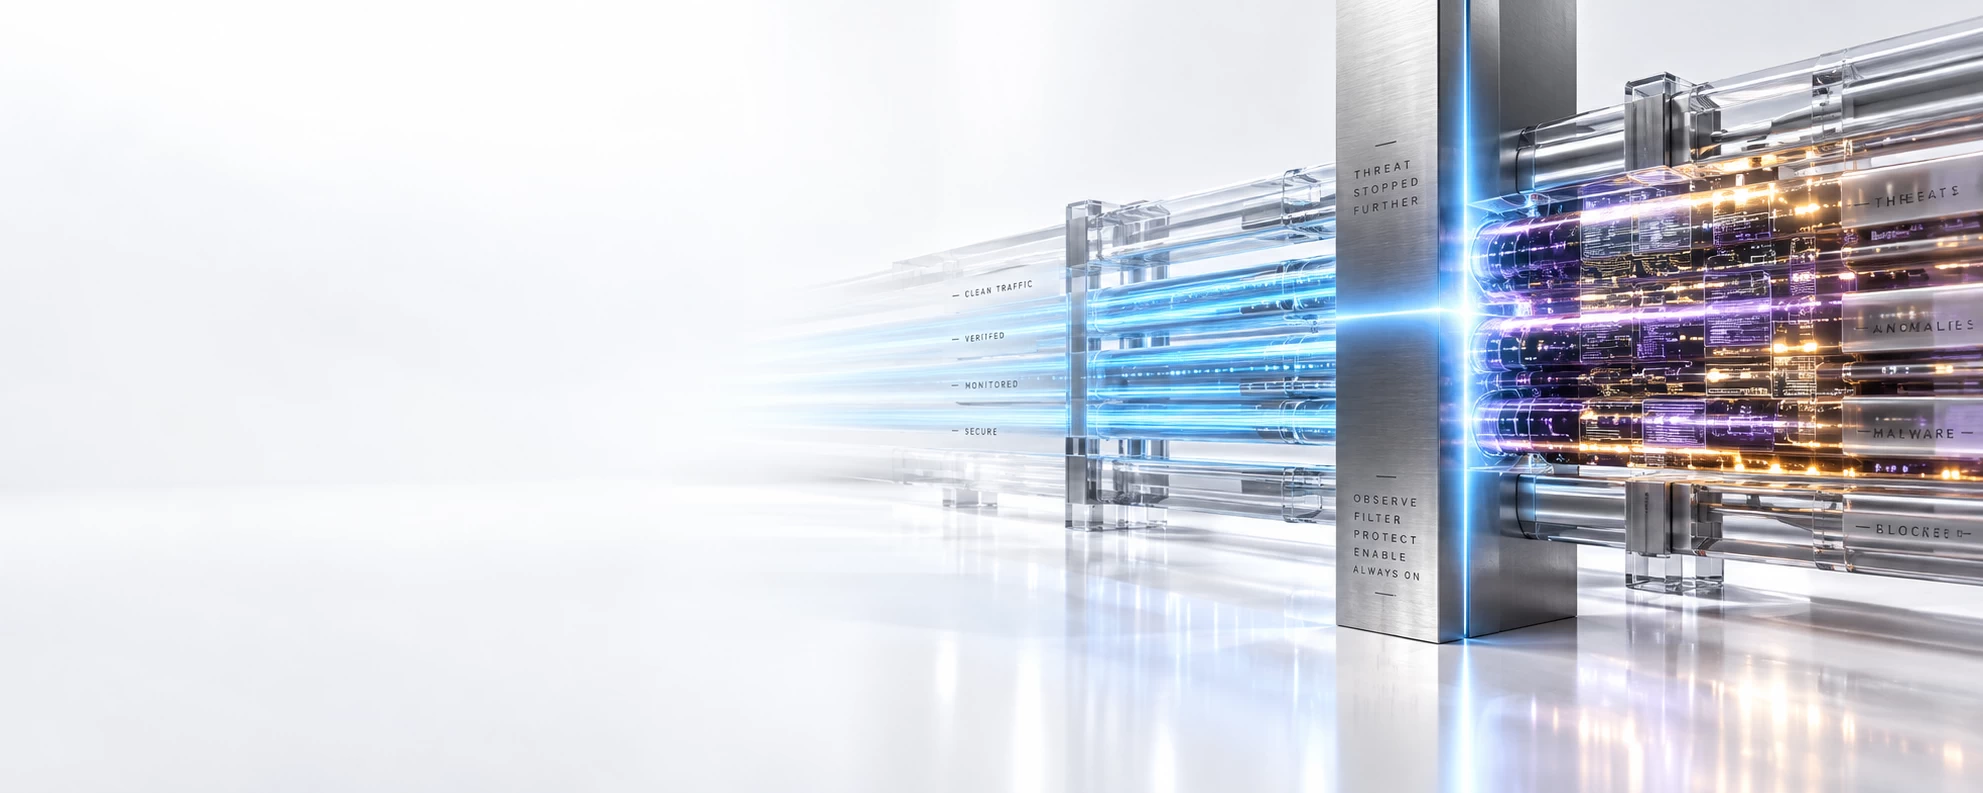
"Why Mature Security Stacks Still Fail Under Pressure" represented by a premium conceptual engineering graphic on a reflective white background illustrating the digital stenographer problem. A matrix of sapphire glass conduits on the right, filled with violet and copper monitoring telemetry streams, is cleanly bisected and sealed by a vertical brushed-titanium blade outlined in a vibrant neon light-blue edge glow, demonstrating visibility transforming into active operational containment while the left side remains pristine for text placement"Why Mature Security Stacks Still Fail Under Pressure" represented by a premium conceptual engineering graphic on a reflective white background illustrating the digital stenographer problem. A matrix of sapphire glass conduits on the right, filled with violet and copper monitoring telemetry streams, is cleanly bisected and sealed by a vertical brushed-titanium blade outlined in a vibrant neon light-blue edge glow, demonstrating visibility transforming into active operational containment while the left side remains pristine for text placement
S10 Group Article series · Why leadership changed

Why Mature Security Stacks
Still Fail Under Pressure

‍Why extensive logging, detailed alerts, and visible investments
still leave incident teams paralysed under a live attack
Article #8
Published: 23 September 2026
By Stan van Gemert | S10 Group
By Stan van Gemert
The CISO series
Executive summary

The previous publication, When One Breach Becomes Everyone’s Problem, showed how a supplier compromise can disrupt organisations that were never attacked, forcing each dependent business to decide what it can disconnect, narrow or keep running while another party controls the recovery.

This article turns to your own security stack. Mature detection, endpoint, identity and monitoring tools can reveal an attack in detail, yet still leave responders without a safe, pre-agreed way to stop it. The decisive gap appears between a credible signal and an executable interruption: which account, session, system or access route can be restricted, who may authorise the move and how much disruption is acceptable before the attacker reaches something more important.

The next publication follows that gap into identity and access. The Door Worked Perfectly. That Was the Problem. examines how valid credentials, approved sessions and familiar workflows can carry harmful behaviour even when every access control appears to have worked.

Maturity can feel reassuring until the first hard decision arrives

A CISO can present a credible maturity story to the board. Endpoint detection is deployed, SIEM correlation is running, threat-intelligence feeds are active and identity monitoring has improved. Backups are tested, the SOC has escalation paths, the response retainer is in place and the audit trail looks responsible.

Those controls matter. They reduce exposure, improve visibility and give security teams better information than they had ten years ago.

During a serious incident, however, the board's question changes. It no longer asks only whether your organisation had the right tools. It asks whether those tools supported timely action once prevention had been bypassed.

Could the attacker be isolated quickly enough? Could critical systems continue? Could compromised credentials or sessions be revoked without breaking essential operations? Could the CISO and executive team authorise containment before the full picture was available?

Many mature environments discover a gap between seeing malicious activity and interrupting it safely. Visibility may be mature even when the interruption path is not.

A mature stack may explain what is happening.
It does not automatically give the incident team a safe, pre-agreed way to interrupt malicious activity

MGM showed why this distinction matters

The MGM Resorts incident is often discussed as an identity, social-engineering or ransomware case. For executive teams, it also illustrates a harder operational problem: a mature organisation can still face blunt choices when legitimate credentials or administrative access are abused.

The central issue is not simply that one control failed, but how far the incident could reach after the first access path opened.MGM was not dealing with an unknown file confined to one endpoint. The incident affected access connected with identity, administration, cloud services and operational systems, making the business disruption inseparable from the technical response.

The relevant question is not whether MGM had invested in security. It is what remained possible once approved access routes were being abused and executives had to contain the consequences while operations were still under pressure.
MGM and the cost of blunt control
MGM is useful because it shows the difference between security visibility and the ability to contain an incident without defaulting immediately to a broad shutdown. Public disclosures described a September 2023 cybersecurity issue that affected parts of MGM's US systems and disrupted business operations. The company estimated an approximately $100 million negative impact to adjusted property EBITDAR for its Las Vegas Strip Resorts and Regional Operations, and less than $10 million in one-time third-quarter expenses for technology consulting, legal fees and other advisers.

Those figures translate an identity and operational-containment problem into board language. The incident showed how quickly misuse of legitimate access can become a business-continuity decision when identity, administration, cloud services and operational systems are connected.

The enduring lesson is broader than improving helpdesk training. Identity and administrative workflows need pre-agreed containment boundaries. A mature stack may reveal that valid credentials or an approved access path are being misused, but it does not automatically provide the proportionate action needed to restrict them without shutting down too much.
View more details chevron A white downward-facing V-shaped chevron on a transparent background.
View more details
Close more details

The digital stenographer problem

Modern tooling can document an attack in remarkable detail without giving the incident team a safe way to interrupt it. The environment can log, correlate, alert, enrich, raise tickets and build a detailed timeline. That information is valuable, but it does not change the outcome while the attacker continues to move. Visibility establishes what responders know. Containment changes what the attacker can still do.

The digital stenographer problem arises when the stack records escalation faster than the executive and incident teams can decide which access, session or system can be restricted. Maturity reports rarely expose that delay. A dashboard may look calm, a response process may look well designed and a playbook may exist, yet the first containment decision can still require input from security, operations, legal, executives and the owner of the affected service. An attacker does not wait for that internal alignment.

Modern tooling may document escalation in detail.
The harder question is whether the incident team can interrupt it safely while it is still unfolding.

Why mature organisations still hesitate

Hesitation is often judged too harshly from the outside. Inside the incident room, hesitation is rarely a simple failure of courage. It usually reflects unresolved operational consequences.

The security team may say: isolate this environment. Operations may ask: which production process stops if we do? The service owner may ask: does this touch customer access? Legal may ask: do we have enough evidence to justify the disruption? Finance may ask: what is the cost of stopping the process now? The board may ask: what happens if we act too early and create the outage ourselves?

Those are responsible questions. The weakness is having to answer them for the first time while the attacker is already inside.

Security maturity feels thinner when the tools, logs and people are present but the interruption path was never designed clearly enough before the incident.

Containment becomes executable when the interruption path, decision owner and acceptable operational consequences have been agreed before the incident.

Attackers exploit legitimate access paths

Ransomware operators do not always begin with behaviour that looks obviously hostile. They may start by using access that already appears normal.

Valid credentials, remote-management tools, supplier access, identity relationships, administrative pathways and cloud integrations can all provide routes created for legitimate business purposes. That makes a mature environment difficult to contain. The attacker may be using a door your organisation built, approved and connected to critical operations.

Detection alone does not resolve the problem. Once abnormal use of an approved route is identified, the CISO and service owner still need to decide whether it can be restricted without damaging the process behind it.

If responders restrict too little, the attacker retains room to move. If they restrict too much, the business may create its own outage. Mature organisations must prepare for that trade-off before an incident.

When an attacker abuses approved credentials or remote-managementroutes, containment becomes a business decision about which access must stop,which operations can continue and what disruption is acceptable to preventwider damage.

The maturity mirage

Extensive tooling can create an impression of readiness that has not yet been tested against a real interruption decision.

A security environment may appear highly prepared because the stack is extensive, reporting is sophisticated, telemetry is rich and investment is visible. But underneath that maturity, the decisive questions may still be unanswered:

  • Which systems can safely degrade?
  • Which identity paths can be narrowed immediately?
  • Which supplier connections are essential and which can be suspended?
  • Which administrative tools should be restricted first?
  • Which business services must keep running even in degraded mode?
  • Who can authorise hard interruption decisions before certainty exists?
  • What evidence is enough to act?

If those answers have not already been agreed, your organisation may have to negotiate its first containment move while the attack is still progressing. This is not a narrow technology failure. It is a failure to design the containment decision before the incident.

MATURITY MIRAGE
Your security stack can be mature while interruption authority and the action path remain immature.
Some organisations therefore appear prepared until the first containment decision carries a real business consequence.

What operational resilience requires

Operational resilience depends on more than knowing what is happening. It requires pre-agreed actions that limit the attacker's reach while essential services continue wherever possible.

Before an incident, the CISO, executive team and service owners should agree:

  • which identities or sessions can be revoked immediately
  • which servers, connections or data paths can be isolated without causing an uncontrolled outage
  • which business services can operate safely in a degraded mode
  • who may authorise each containment action
  • what evidence threshold is sufficient to act
  • how the decision and its operational effects will be recorded

Those agreements extend security maturity beyond prevention and detection. Prevention lowers the chance of entry, detection improves awareness, backups support restoration and response teams investigate and coordinate recovery. None of those functions automatically creates the authorised action that stops an active intrusion from becoming wider operational damage.

What containment changes

An operational containment layer matters when the security stack has identified malicious activity but responders still need a proportionate way to interrupt it.

Our Ransomware Containment platform complements EDR, SIEM, identity controls, backups and response services. It agentlessly monitors file activity across the protected data environment and isolates the responsible user, session or device once illegitimate encryption begins.

Additional Server Intrusion Protection and Virtual Server Protection features extend the platform to compromised server access and attacks directed at supported VMware, vSphere, ESXi and Hyper-V environments.

For incident, infrastructure and executive teams, the value is practical: specific harmful activity can be contained while they determine which services remain safe to operate and what the wider response requires.

A mature stack becomes operationally useful when detection can be translated into an authorised containment action before damage spreads.

CONTAINMENT IMPLICATION
The first hour should not depend on improvising whether interruption is allowed.
It should follow pre-agreed actions that the CISO, executive team and service owners understand and can authorise.

Pressure-test question

If valid credentials or remote-management access were abused inside your environment tomorrow, would your organisation know which accounts, sessions or systems could be isolated before complete certainty exists?

Would the CISO have the authority, evidence threshold and operational support to act before the attacker reaches additional systems or disrupts essential services?

The next horizon

The next publication moves from the maturity of the stack to the legitimacy of the access it is monitoring. "The Door Worked Perfectly. That Was the Problem." examines how valid credentials, approved sessions and familiar workflows can carry harmful behaviour even when the access controls themselves appear to have worked. The challenge is to interrupt what the session is doing before legitimate permission becomes wider operational damage.

Hear first when a new S10 Group release is published

Would you like to receive a short note when S10 Group publishes a new article or newsletter?

Leave your name and email address below. We will send a short update when a new release is available, with a brief summary and a direct link to the publication.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

Coming soon

Friday 25 September: WAM03: "The Door Worked Perfectly. That Was the Problem."

Monday 28 September: R03: "When Trusted Systems Become the Attack Path"

Further readings