About S10 represented by a cinematographic shot from inside a hypermodern, glass boardroom or command center at a great height, looking out over an abstract, illuminated skyline of a digital metropolis in the evening. Inside, the interior is dark and minimalist: a sleek,empty conference table made of dark glass in which the data lines of the outside world subtly reflect. The atmosphere is serene and intellectual. It exudes the presence of strategic thinking.About S10 represented by a cinematographic shot from inside a hypermodern, glass boardroom or command center at a great height, looking out over an abstract, illuminated skyline of a digital metropolis in the evening. Inside, the interior is dark and minimalist: a sleek,empty conference table made of dark glass in which the data lines of the outside world subtly reflect. The atmosphere is serene and intellectual. It exudes the presence of strategic thinking.

About S10 Group

Practical expertise.
Trusted partnerships.
Solution-led delivery.

Control matters most when certainty is gone

Cyber incidents are rarely experienced as clean technical events. They become moments of uncertainty, where systems are still running, but trust is no longer clear, and every decision carries operational risk.

This is where leadership is tested. Not on prevention, but on the ability to stay in control. S10 Group exists to support organisations in exactly that moment.

Our perspective: resilience is not a tool, it is control under pressure

Most organisations have invested heavily in prevention and detection.

Yet in real incidents, the critical gap appears after initial access, when visibility exists, but decisive control is still missing.

We focus on that gap.

Because:

  • Detection does not stop spread
  • Backups do not prevent disruption
  • Compliance does not guarantee control

Resilience is defined by what happens after something gets inside.

Our role: enabling control when it matters most

S10 Group supports organisations in maintaining control during active cyber incidents.

We do this by:

  • Validating how environments behave when prevention is bypassed
  • Enabling containment of ransomware and lateral movement
  • Preventing data theft from becoming leverage
  • Preserving operational continuity under pressure

Our platform operates alongside existing security investments,

extending them into the moment where control is most at risk.

How we work

Our approach is structured, controlled, and designed for critical environments.

It typically includes:

  1. Resilience validation
    A controlled scenario that shows how your environment behaves when something gets inside.
  2. Platform demonstration
    A clear view of how containment is achieved in practice.
  3. Alignment with your environment
    Integration with existing security, infrastructure, and governance models.
  4. Controlled deployment
    Implemented without disruption to ongoing operations.

This ensures that decisions are based on observed reality, not assumptions.

What sets S10 Group apart

  • Focus on the inside phase of an attack
  • Built for containment, not just visibility
  • Designed for operational continuity
  • Works alongside existing security stacks
  • Enables defensible decisions under pressure
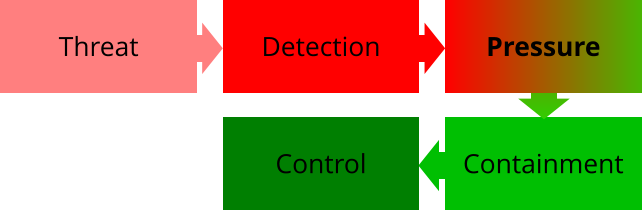
A process flow diagram with arrows showing the progression from Threat to Detection, Pressure, Containment, and ultimately achieving Control.A process flow diagram with arrows showing the progression from Threat to Detection, Pressure, Containment, and ultimately achieving Control.

S10 Group was founded in 2013 as a consultancy focused on improving efficiency, reducing unnecessary cost, and strengthening operational performance.

As the threat landscape evolved, the focus shifted toward cybersecurity — specifically the ability to maintain control once prevention is bypassed.

See how control holds when pressure rises
Contact us and run a FREE resilience assessment
HOW OUR PLATFORM WORKSRUN A RESILIENCE ASSESSMENT