Conceptual 3D visual of five sapphire-glass prisms sorting a red threat beam into orderly blue pathways, representing executive decision control during a cyber incident.Conceptual 3D visual of five sapphire-glass prisms sorting a red threat beam into orderly blue pathways, representing executive decision control during a cyber incident.

The Decisions That
Define The Outcome

Ransomware does not become a crisis only because it enters.
It becomes a crisis because of what happens next.

Deciding before certainty

The most consequential choices in a cyber incident are often made before the full situation is known. Systems may still be running, access may still work and technical teams may have enough evidence to be concerned without being able to reconstruct the entire attack.

That is when your organisation must decide whether to restrict an account, isolate a system, pause a supplier connection or accept a limited disruption to prevent a larger one. Delay is also a decision because it leaves the current path open while the incident continues to move.
The attack creates the pressure.
The quality and timing of your decisions shape the outcome.

The moment the incident becomes a decision crisis

A privileged identity behaves differently. A supplier route carries unusual activity. A data transfer exceeds its normal pattern. The security team can see enough to justify concern, but the operational effect of intervention is still uncertain.

Hesitation begins because the next move has two possible costs. Acting may interrupt an important service; waiting may allow the attacker to reach something more important. Your organisation needs a defined threshold for intervention, an authorised decision-maker and a containment action whose operational effect is understood.

The decision cannot wait for complete certainty,
but it must still be proportionate to the evidence available.

Why the decision window has collapsed

Attackers can use valid credentials, administrative tools and connected supplier routes before the incident produces a visible outage. Data may be staged and privileges may expand while your teams are still validating the first signal.

The available decision window is therefore measured against attacker progression, not against the time needed for a complete investigation. Your executive team must know which actions can be authorised on a credible signal, which services may be degraded and when the cost of waiting exceeds the cost of intervention.

DECISION PRESSURE
Credible signal → operational consequence assessed → authority confirmed → proportionate action executed

The five decisions that shape the outcome

Every incident is different, but executive pressure often concentrates around five decisions.

Decision
Why it matters under pressure
1. Which access and assets can remain in use
Identify the identities, sessions, systems, recovery points and supplier routes that have enough evidence behind them to remain operational. Anything else needs restriction, additional verification or an explicit risk decision.
2. What do we restrict first
Choose the narrowest action that materially changes the attacker's path: an account, session, server, segment, shared service or external connection. The decision should include its operational effect and the condition for reversal.
3. When is recovery safe to start
Recovery should begin only after the relevant access paths are contained and the restoration point has been validated. Speed without those conditions can reintroduce the attacker or contaminate the rebuilt environment.
4. Has data already changed the incident
Likely exfiltration expands the response beyond system availability. The executive team must consider affected people, legal obligations, extortion leverage and communication while containment continues.
5. What can we communicate now
State what is known, what remains under investigation, what action has been taken and when the next update will follow. Avoid filling evidence gaps with reassurance that may later need to be withdrawn.
Hesitation does not come from weakness.
It comes from uncertainty, and lack of executable control.

Why hesitation becomes expensive

An attacker does not wait for better governance. Delay is not neutral. It changes the shape of the incident.

When decisions wait for perfect confirmation, spread may continue, data exposure may grow, privileged pathways may stay open longer and recovery may become more complex than it needed to be. This is where mature organisations still struggle. Not because nobody saw the signal. Because the hard move was still waiting for permission, proof or a safer moment that never arrived.

THE PATH CHANGES
Detection → Delay → Escalation
Detection → Action → Containment

What these decisions are really testing

What these decisions are really testing

The five decisions test whether your operating model can convert incomplete evidence into proportionate action. Your organisation needs:

  • authority that is clear before full certainty exists;
  • a defined evidence threshold for restricting access or service;
  • containment actions with understood operational effects;
  • communication that distinguishes confirmed facts from open questions;
  • recovery gates that prevent premature restoration; and
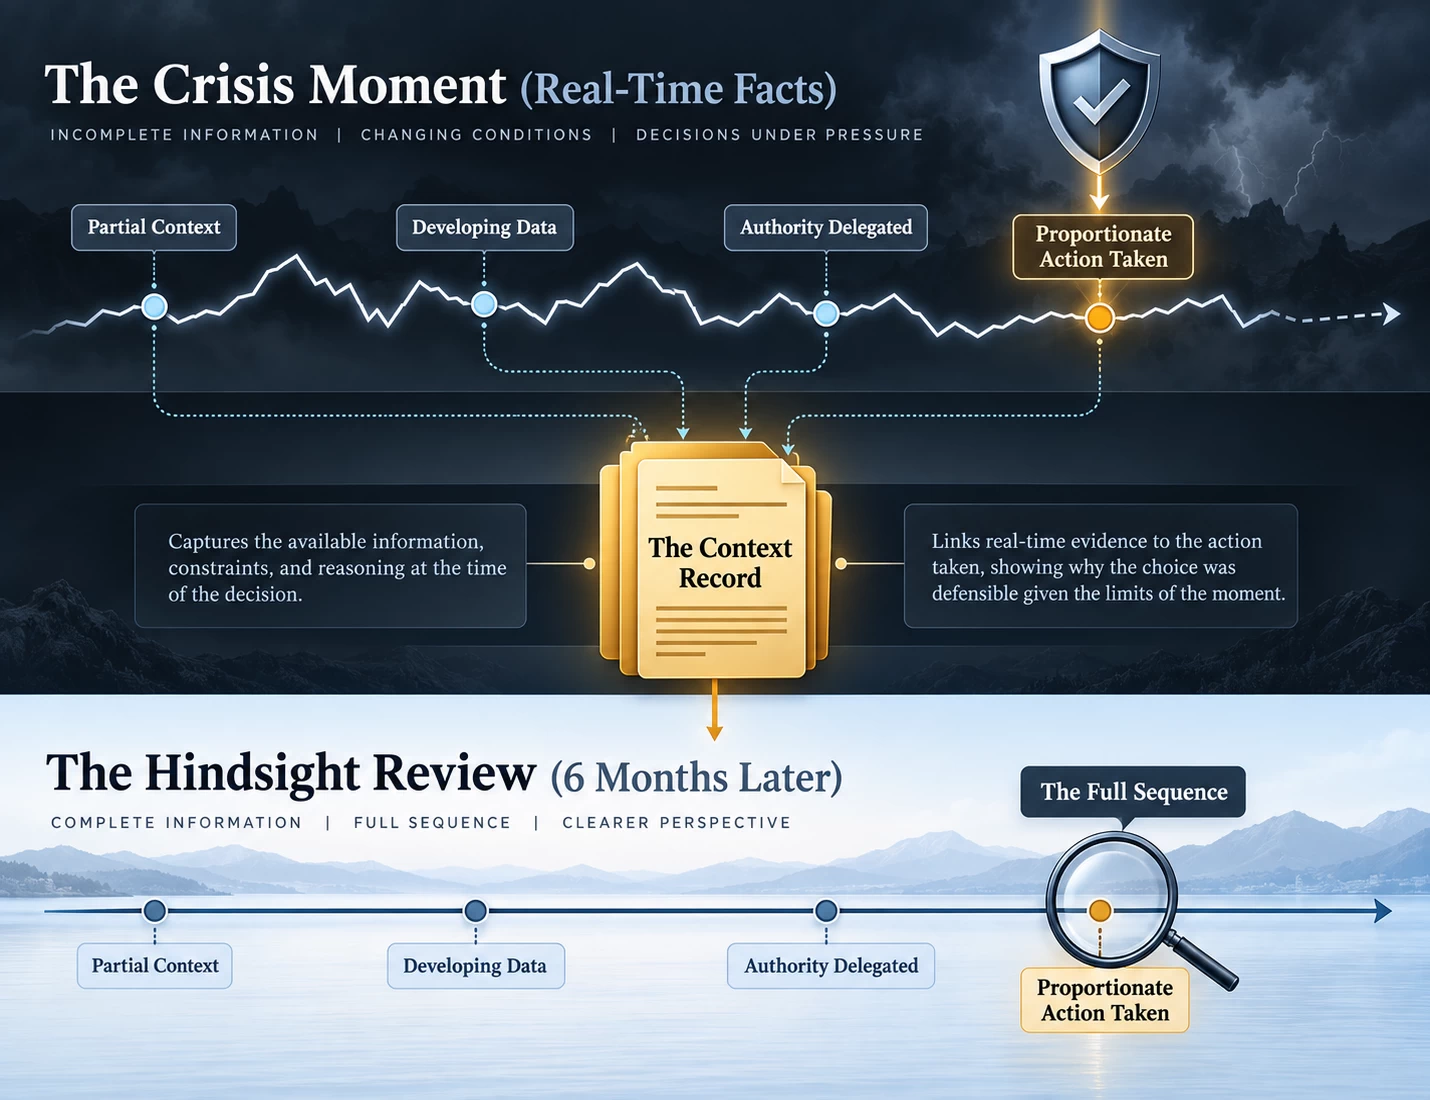
  • a decision record preserving what was known, who held authority and why the action was proportionate.

The decision must survive hindsight

During an incident, leaders act on the facts available at that moment. Months later, the same choices may be reviewed as though the full sequence had already been visible. That is why the decision record matters: it should preserve what was known, when it became known, who held authority, which risks were considered and why the action taken was proportionate.

A clear record does not remove accountability. It makes accountability traceable and defensible by showing how a decision related to the evidence available at the time. The ability to preserve that context must therefore be designed before the incident, rather than reconstructed afterwards.

For the wider implications of disclosure, accountability and defensible governance, continue to Legal & Governance.

If a decision is challenged six months from now, can your organisation demonstrate what was known at the time, who held authority and why the action was proportionate?

‍

Cyber crisis timeline showing a context record that makes proportionate action traceable from real-time uncertainty to a later hindsight review.

The most important decision is made before the incident

Your organisation should decide in advance which services receive priority, who may authorise containment and what evidence is sufficient to act. Those choices determine whether the first serious signal becomes an operational move or another escalation meeting.

The preparation is practical: defined authority, known service dependencies, tested interruption paths and a decision record that can later explain why action was taken.

The first live decision is safer when its authority, boundaries and operational consequences have already been agreed

Where control is lost

Control is rarely lost because of a total absence of security tools. It is lost when authority is unclear, trust is uncertain, actions are not executable, or the environment offers no safe operational move once malicious behaviour is already in motion.

The decision problem and the containment problem are closely connected. The better your organisation can interrupt spread safely, the easier it becomes to make proportionate decisions under pressure.

CONTROL LOSS PATTERN
Unclear trust → delayed authority → wider spread → fewer good options

What changes the outcome

When decisions become executable, the trajectory changes.

What changes
Why it matters
Spread is limited
The blast radius narrows before the attacker gains more freedom.
Data exposure is reduced
The chance of longer-term leverage and customer harm falls.
Operations remain more intact
The organisation preserves room to continue, even if in degraded mode.
Decision-makers gain time
Better decisions become possible when harmful activity has been restricted and the operating field is smaller.
Executable control improves the quality of the decisions that follow

From decision to executable control

A decision changes the outcome only when teams can execute it. Our platform complements your existing security stack by giving authorised responders a practical way to interrupt ransomware encryption and malicious movement, restrict affected access and protect supported virtual infrastructure while the wider investigation continues.

The executive team still determines the acceptable operational boundary. Our role is to translate that boundary into a precise containment move before spread, exposure or infrastructure damage removes the remaining options.

The result is not immediate certainty. It is a smaller incident field, clearer evidence about what was contained and more time for the decisions that follow.

Request a ransomware resilience assessment

See whether containment changes the outcome once encryption begins

Our controlled ransomware resilience assessment compares how several ransomware-encryption scenarios unfold with your existing security controls left active: first without our containment layer and then with it enabled.

The assessment focuses on one practical, observable question: "can active encryption be contained before its impact spreads further?"

Further readings