Conceptual 3D visual of leaning frosted-glass blocks stabilised by a titanium pillar with a blue edge glow, representing reduced human pressure during a cyber crisis.Conceptual 3D visual of leaning frosted-glass blocks stabilised by a titanium pillar with a blue edge glow, representing reduced human pressure during a cyber crisis.

Human Impact

When a cyber incident becomes real,
the impact is not only operational. It becomes personal.

The human toll behind the timeline

Cyber incidents are usually reported through systems affected, hours of downtime and recovery milestones. People experience them through responsibility, uncertainty and sustained pressure.

An administrator must decide whether isolation is safe. A service desk answers questions before facts are complete. An executive authorises disruption that may later be scrutinised. A customer, patient or employee waits to learn whether personal information has left your environment.

Those are not secondary effects. They are part of the incident and they influence judgement, communication and recovery.
The incident may begin in technology.
People carry its decisions and consequences.

The incident enters the room

A ransomware attack rarely arrives as a complete technical picture. It appears as an alert, a locked file, unusual account activity or a service that no longer behaves as expected. The first visible consequence may be a room of people who know that the next decision could either contain the problem or widen the disruption.

Should a service be isolated? Can a workflow continue? Who may interrupt operations? Which systems and sessions have enough evidence behind them to remain in use? What can be said to employees, customers, suppliers or regulators while the facts are still changing?

Each question assigns responsibility before certainty exists. The human burden begins at that point, not after the technical response is complete.

What people carry while the incident is still moving

The attacker creates the incident. Unclear authority, incomplete facts and sustained operational demand determine how much pressure people must absorb.

Responsibility without full control

People are expected to act and explain while key facts and dependencies remain unresolved.

Sustained cognitive pressure

Incident teams may work for days with disrupted sleep, repeated escalation and less time to check each decision.

Cross-functional friction

Security, operations, legal, communications and service owners may see different risks and timelines in the same decision.

Frontline exposure

Service desks, clinicians, customer teams and managers may face affected people before a reliable external account is ready.

Executive accountability

Decisions may later be reviewed by boards, regulators, customers, insurers or the public with more information than was available at the time.
The pressure starts while the incident is still moving and continues until people can rely on a stable operating picture.

The first hour is a human burden

The first hour is often described as a race against time. That is true. But for the people involved, it is also a race against ambiguity.

Who has authority to act before certainty exists? What counts as enough evidence to isolate, restrict or degrade a service? What operational impact is acceptable if waiting may make the incident worse?

When those answers have not been agreed in advance, pressure does not disappear. It moves onto people. They carry the delay, the doubt and the fear that either action or inaction may deepen the harm.

If authority is unclear, people carry the delay.

When data exposure makes it personal outside the organisation

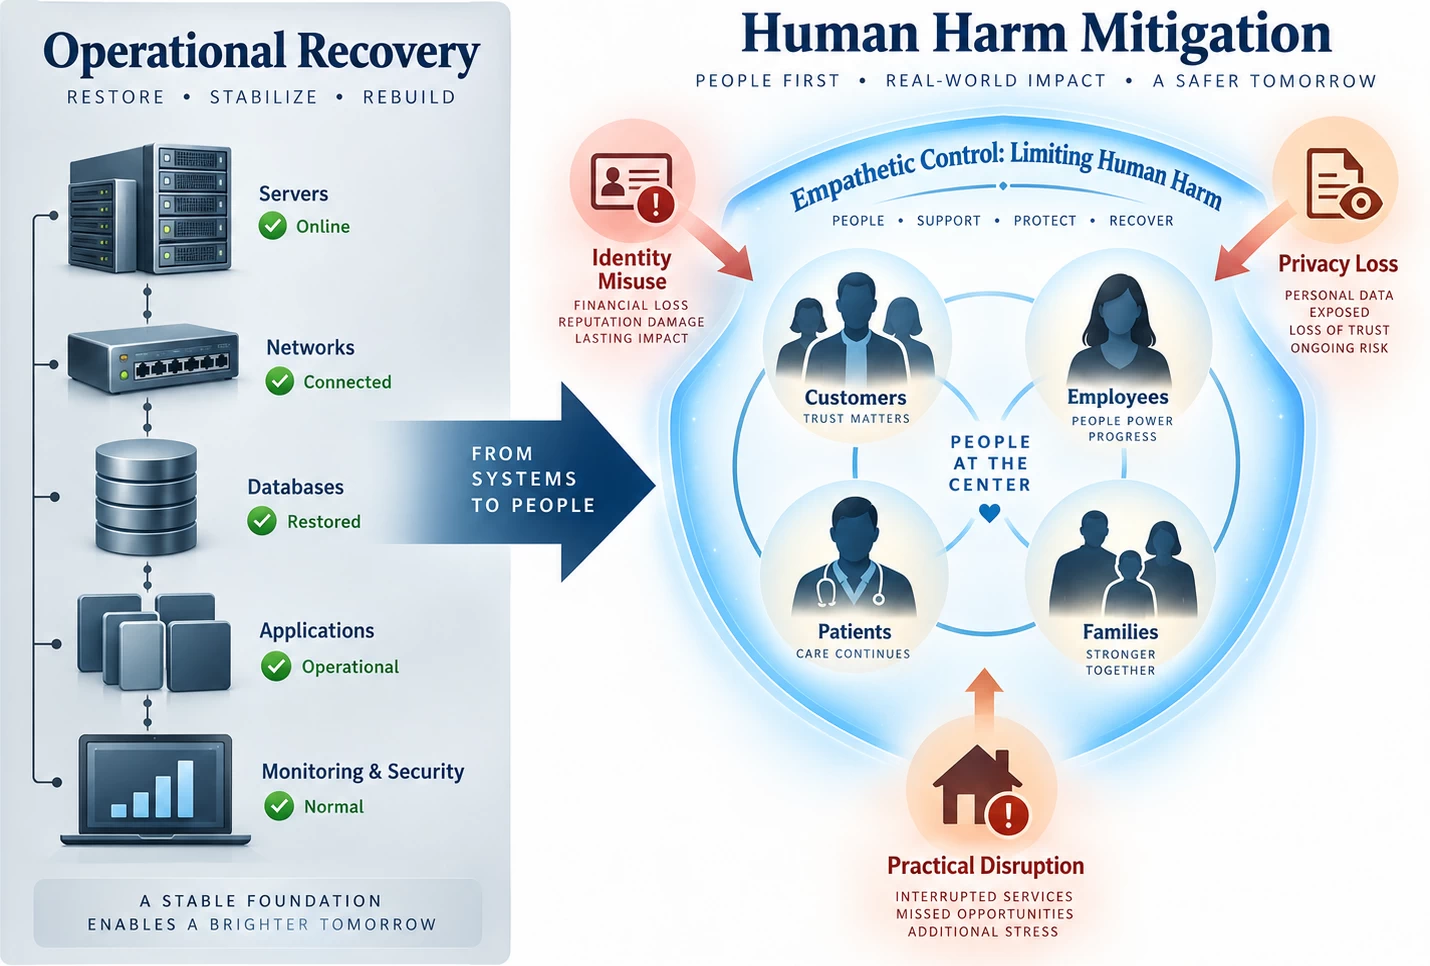
Stolen data transfers part of the burden to people who had no role in the technical failure. Customers, patients, employees and families may face fraud, identity-document replacement, privacy loss, intimidation or the recurring need to prove that misuse was not their action.

Inside your organisation, teams understand that the consequences can continue after systems return. They must establish who is affected, prepare practical guidance and communicate without minimising harm or claiming facts the investigation has not yet confirmed.

The knowledge that other people may carry the incident for years changes the weight of containment and communication decisions from the first hours onwards.

Cyber incident impact diagram showing how restored systems still leave customers, employees, patients and families exposed to identity misuse and privacy loss.

Recovery does not always restore people

Systems can come back online faster than confidence returns.

After a serious incident, people may carry exhaustion, second-guessing, loss of confidence, fear of recurrence and the residue of decisions made under incomplete facts. Teams may become more cautious. Leaders may hesitate sooner. Normal processes may feel less trustworthy than they did before.

This is one reason recovery plans can underestimate the real aftermath. They often describe how systems return. They do not always describe how people recover from carrying the incident.

Recovery restores systems.
It does not automatically restore people.

Executive responsibility is personal too

Executives carry a different form of pressure. They must authorise actions with operational consequences, explain uncertainty and remain accountable for decisions that may later be judged with the benefit of a complete timeline.

Board-level accountability

The record should show what was known, who held authority and why the action was proportionate at that moment.

Operational responsibility

Executives must balance containment, continuity, evidence preservation and possible harm to customers or employees.

Communication pressure

Silence can create confusion, while premature certainty can damage credibility when the facts change.

Personal judgement

The hardest choices often arrive before enough information exists to make anyone comfortable with them.

What changes the human outcome

A serious incident will still create pressure. The avoidable burden grows when authority is unclear, harmful activity continues and people must improvise around an expanding technical problem.

Clearer authority

Teams know who can approve isolation and which operational consequences have already been accepted.

A smaller incident field

Earlier containment leaves fewer systems, customers and teams inside the response.

Better evidence

People can explain decisions and communicate from verified facts rather than filling gaps under pressure.

A shorter tail

Reduced spread and exposure mean fewer consequences that employees and affected individuals must manage later.
Containment cannot remove every human consequence,
but it can prevent more people from being drawn into an incident that is still expanding.

Where our platform fits

Our platform gives authorised responders a practical containment move while an incident is active. It helps interrupt ransomware encryption and malicious movement before more people, services and systems are drawn into the response.

Ransomware Containment is the central platform. Server Intrusion Protection and Virtual Server Protection are additional features that extend protection to compromised administrative access and supported virtual infrastructure.

DETECT
Recognise malicious behaviour after entry and identify the affected access, session or system.

CONTAIN
Restrict ransomware encryption, malicious movement and exposure pathways before escalation widens.

STABILISE
Preserve evidence and operational room while technical, executive and frontline teams manage the wider response.

Our platform does not remove the responsibility people carry; it prevents an unfolding incident from creating an avoidable operational burden.

The resilience benchmark

Reduce avoidable escalation before more people carry the consequence.

Our controlled ransomware resilience assessment compares file-encryption scenarios with your existing security controls left active, first without Ransomware Containment enabled and then with it enabled. It tests whether active encryption can be isolated before it spreads further.

Our automated assessment does not directly test human readiness, decision authority or technical vectors such as lateral movement, data exfiltration, or infrastructure protection. Instead, those critical dimensions and their broader governance implications can be definitively evaluated via a tailored presentation during the session.

Further readings