
Resilience assessment information represented by a team of three cybersecurity specialists—two men and a woman—gathered closely around a computer workstation in a dimly lit, dark-toned control room at night. They are wearing casual business attire and spectacles, looking intently at a monitor displaying code and active data logs with serious, highly focused expressions as one team member points directly at the screenResilience assessment information represented by a team of three cybersecurity specialists—two men and a woman—gathered closely around a computer workstation in a dimly lit, dark-toned control room at night. They are wearing casual business attire and spectacles, looking intently at a monitor displaying code and active data logs with serious, highly focused expressions as one team member points directly at the screen

FREE Resilience Assessment

A controlled resilience assessment for when prevention is bypassed.

FREE RANSOMWARE RESILIENCE ASSESSMENT

Test your existing preventive controls against a domino-effect encryption breach in your own environment, and discover the added value of our platform.

Our controlled ransomware resilience assessment shows how your existing environment responds when ransomware behaviour begins to move after prevention has been bypassed.

FREE FOR ORGANISATIONS WITH MORE THAN 250 EMPLOYEES

Start your assessment now →

The question a security stack cannot answer on paper

Most organisations already have prevention, endpoint protection, monitoring, backups and incident-response plans. Those investments reduce risk and create visibility. They should be respected, not dismissed.

The unresolved question appears after something gets past the first line of defence.
Can your organisation still prevent one compromised point from becoming a wider operational problem?
Can it act while the situation is moving, or only explain what happened after the fact?

The assessment turns that concern into something observable. It places controlled ransomware behaviour into an agreed test environment and shows how the surrounding controls respond. The purpose is not another maturity score. It is to find out whether a usable intervention exists when prevention is no longer the whole answer.

RESILIENCE IS NOT PROVEN BY WHAT IS INSTALLED
It is proven by what can still be controlled when malicious behaviour starts to move.
Assessment lens
What it shows
Where control holds - and where it weakens
Observe how the prepared environment responds when controlled ransomware behaviour begins. The assessment distinguishes controls that change the outcome from controls that only make the problem visible.
How quickly local activity can become wider pressure
Follow the behaviour through the agreed test resources so that escalation paths become visible before a real incident exposes which systems, data paths or dependencies are reachable.
Whether containment changes the trajectory
Evaluate whether suspicious encryption or propagation can be bounded early enough to preserve more of the environment. The decisive proof is not another alert. It is an action that prevents a larger cascade.

What our assessment puts under controlled pressure

Our assessment uses controlled ransomware simulations in a prepared, isolated test environment. The detailed scope is agreed before the session so the activity remains relevant, observable and contained. Production systems are not used as the test environment.

  • Controlled encryption behaviour - observe how the environment responds when simulated malicious encryption begins against agreed test resources.
  • Propagation within the agreed scope - see whether activity remains local or can reach additional test resources before an effective response is available.
  • The response of existing controls - understand what the current environment detects, interrupts or allows to continue under controlled pressure.
  • The effect of executable containment - evaluate whether a containment action can reduce reachable scope and change the simulated incident path.
SCOPE CONTROL
The final assessment scope is confirmed during the scoping conversation.
This keeps the public promise precise while allowing the technical session to reflect the organisation's environment.

The proof is the changed trajectory

The assessment is not designed to prove that every existing control has failed. It creates a controlled comparison between the protection already in place and the additional effect of an executable containment response.

Your existing controls under pressure
When containment becomes executable
The current security environment remains the starting point. The assessment observes what it sees, what it stops and what continues once the simulated behaviour begins.
Containment is evaluated as an operational action, not another notification. The question is whether suspicious behaviour can be bounded before the reachable scope becomes materially larger.
THE VALUE IS NOT A PASS MARK
It is knowing which action changes the outcome.

How our assessment works

Our assessment is conducted remotely with one or more S10 Group security experts. Technical preparation is agreed before the session, and all simulation activity remains inside the controlled test environment.

1
Prepare the environment

We confirm the intended scope, walk your team through the prerequisites and answer initial questions. Your technical team prepares the agreed isolated test environment before any simulation takes place.
2
Configure the assessment

With your local technical contact, S10 completes the agreed remote configuration and verifies that the test environment is ready. Detailed configuration guidance is shared after the request has been scoped.
3
Run controlled simulations

Controlled ransomware scenarios are exercised while your team observes how the environment and response controls behave. The purpose is to make the escalation path and available intervention visible.
4
Understand the result

The assessment generates a diagnostic report. S10 then reviews the result with your team so that what happened in the test environment becomes a practical input for resilience and containment decisions.
FREE FOR ORGANISATIONS WITH MORE THAN 250 EMPLOYEES
It is knowing which action changes the outcome.

Designed for a controlled environment

  • The simulation is performed in a prepared, isolated test environment rather than against production.
  • The session can be conducted remotely, allowing the relevant team to observe and ask questions without turning the assessment into an operational deployment project.
  • The initial request requires business contact and qualification information only. Confidential infrastructure, security or live-incident details should not be entered into the request form.
  • Once eligibility and scope are confirmed, S10 shares the practical prerequisites and agrees the appropriate technical participants and timing with your team.
Question
Answer
Does it replace our existing security tools?
Containment is evaluated as an operational action, not another notification. The question is whether suspicious behaviour can be bounded before the reachable scope becomes materially larger.
Will production systems be tested?
No. The assessment is performed in a controlled, isolated test environment. The detailed prerequisites are agreed with your team before the session is scheduled.
Who should be involved?
A technical contact is needed to prepare and observe the test environment. Other stakeholders can join the review where they will help interpret the result and decide what happens next.
What does free cover?
The standard resilience assessment is free for organisations with more than 250 employees. S10 Group confirms eligibility, the intended assessment scope and the required preparation before any session is agreed.
Do we need to share sensitive technical information in the form?
No. The form starts a scoping conversation. Please do not include confidential infrastructure, security or live-incident information in the initial request.

Would you know where control changes?

A live incident is the most expensive place to discover that detection did not become interruption. This assessment shows where the current environment holds, where the incident path remains open and whether containment can still stop the cascade.
REQUEST YOUR FREE RESILIENCE ASSESSMENT

Start with a short scoping conversation and contact us.

Or use the "REQUEST RESILIENCE ASSESSMENT" button below and submit your request to begin your resilience assessment.

The standard assessment is free for organisations with more than 250 employees and is performed remotely in a controlled, isolated test environment.
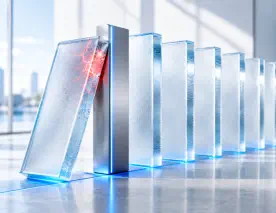
Resilience assessment represented by a domino effect of glass blocks symbolizes the cascading crisis (the chain reaction of an attack).The first glass block falls over and shows cracks and red stress lines (the initial contamination/data breach). But instead of the whole line collapsing,there stands that unshakable one, brushed metal barrier with the light blue neon line.This one absorbs the blow,absorbs pressure and maintains control, so that all underlying glass blocks (the rest of the critical infrastructure and business operations) remain perfectly intact and unaffected.