The paradox of the complete security stack
Most serious incidents do not begin in organisations that ignored cybersecurity. They begin in environments with prevention programmes, identity controls, monitoring, backups, awareness training and an approved incident-response plan.
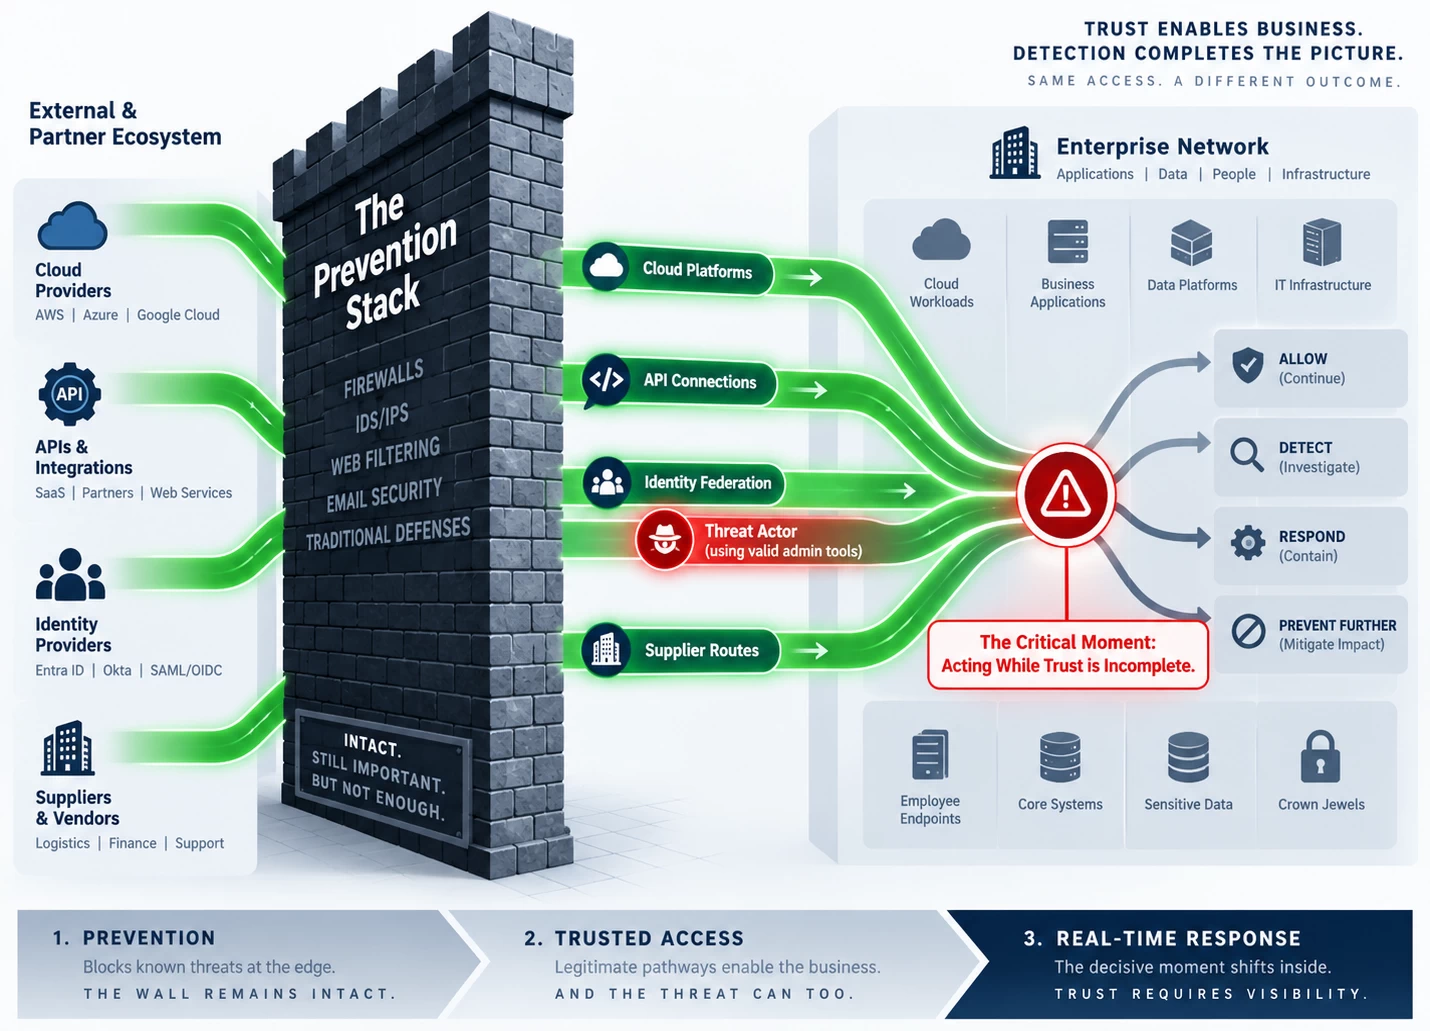
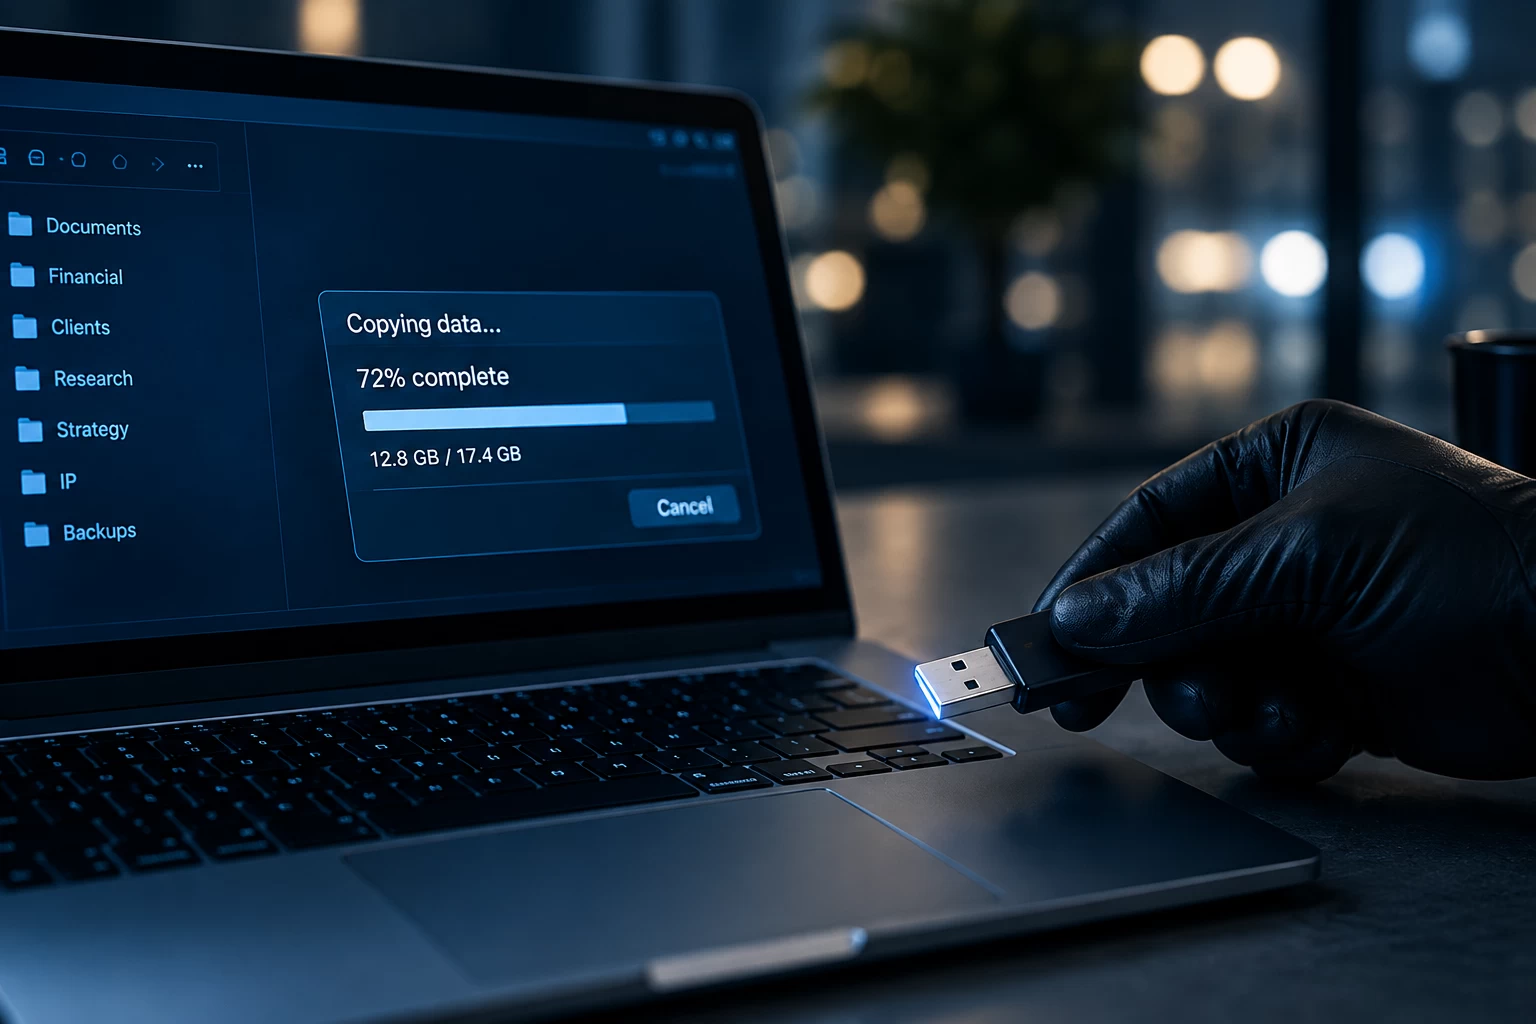
Those measures reduce the likelihood of entry and may expose malicious activity earlier. They cannot determine the outcome once an attacker is already using a credential, session, supplier connection or administrative path inside the environment.
At that point, the decisive capability is post-entry control: whether your organisation can restrict harmful activity before it reaches more systems, data or operational dependencies.