Conceptual 3D visual of an outbound sapphire-glass data conduit where a volatile threat stream is blocked by a titanium barrier, representing data exposure control.Conceptual 3D visual of an outbound sapphire-glass data conduit where a volatile threat stream is blocked by a titanium barrier, representing data exposure control.

What Happens
When Data Leaves Your Organisation

When sensitive data has already crossed the boundary,
the incident no longer stays inside the organisation.

The illusion of a quiet incident

The visible disruption may still be limited. Systems may be running, customers may know nothing and the incident may appear containable inside the technical team.

Once data has been copied, staged or removed, the consequence is no longer confined to your environment. Your organisation has lost exclusive custody of information that may be disclosed, traded or reused long after systems have been restored.

Encryption can be reversed through recovery.
Data exposure cannot be recalled.

The incident leaves the building

A ransomware incident used to be imagined as a locked-screen problem. Files were encrypted. Operations stopped. The ransom note appeared. The organisation then faced a brutal but relatively visible question: can we restore?

Modern incidents often move differently.

Data may leave before disruption becomes obvious. Sensitive information may be searched, staged and copied while the organisation still believes the main issue is access, availability or an isolated technical signal.

That is the moment the incident stops being only internal.

It now reaches people who never touched the system: customers, patients, employees, suppliers, partners and affected individuals whose records become part of someone else’s leverage.

The question changes from “Can we restore the service?” to “What has already left, who can be harmed, and what can still be prevented from getting worse?”

Why stolen data changes everything

Stolen data has a different character from encrypted data.

Encrypted data may be restored from backup, rebuilt from a clean environment or reconstructed through a recovery process. Stolen data does not return to a trusted state because the organisation can no longer prove who has it, how many copies exist, where it may move next or how it may be used later.

That is why data theft changes the balance of power. The attacker no longer needs only access to your environment. They now hold something that can create pressure outside it.

A restored system can look clean. The stolen data does not come back.

This is the uncomfortable difference many organisations discover too late. Technical recovery can make the environment usable again. It does not erase the exposure, the legal questions, the customer anxiety or the future misuse risk.

Backups do not remove leverage

Backups matter. Clean recovery matters. Operational continuity matters.

But backups solve only part of the problem. They can help restore availability. They do not remove the attacker’s leverage over copied information.

Once sensitive data is outside your organisation, payment provides no reliable proof of deletion. A criminal assurance cannot establish how many copies exist, whether the information was shared or whether it will be reused later.

Payment may change the immediate pressure. It cannot restore exclusive custody of the data.

What this means for people

For the organisation, data exposure may appear first as a breach notification, a legal question or a communications problem.

For the people behind the records, it can become something much more personal.

A leaked file can become a fraudulent subscription. A copied document can become an identity check somewhere else. A phone number, address, date of birth or account detail can be used repeatedly in ways the affected person has to keep explaining, blocking or correcting.

And when the data is more sensitive, the impact can be deeper still.

Health records, therapy notes, financial information, employment data, identity documents or details about children are not just “records”. They are parts of someone’s life that were never meant to become public pressure.

What exposure can create
What it means in practice
What exposure can create:
Identity misuse
What it means in practice:
Individuals may have to defend themselves against fraud they did not create.
What exposure can create:
Repeated verification burden
What it means in practice:
Affected people may need to monitor accounts, challenge misuse and prove they are the victim.
What exposure can create:
Loss of privacy
What it means in practice:
Sensitive information may be impossible to make private again.
What exposure can create:
Long-tail anxiety
What it means in practice:
The incident can continue for people long after the organisation has moved into recovery.
For individuals, a data breach is often not a single event.
It is the beginning of a longer problem.

Your organisation loses more than confidentiality

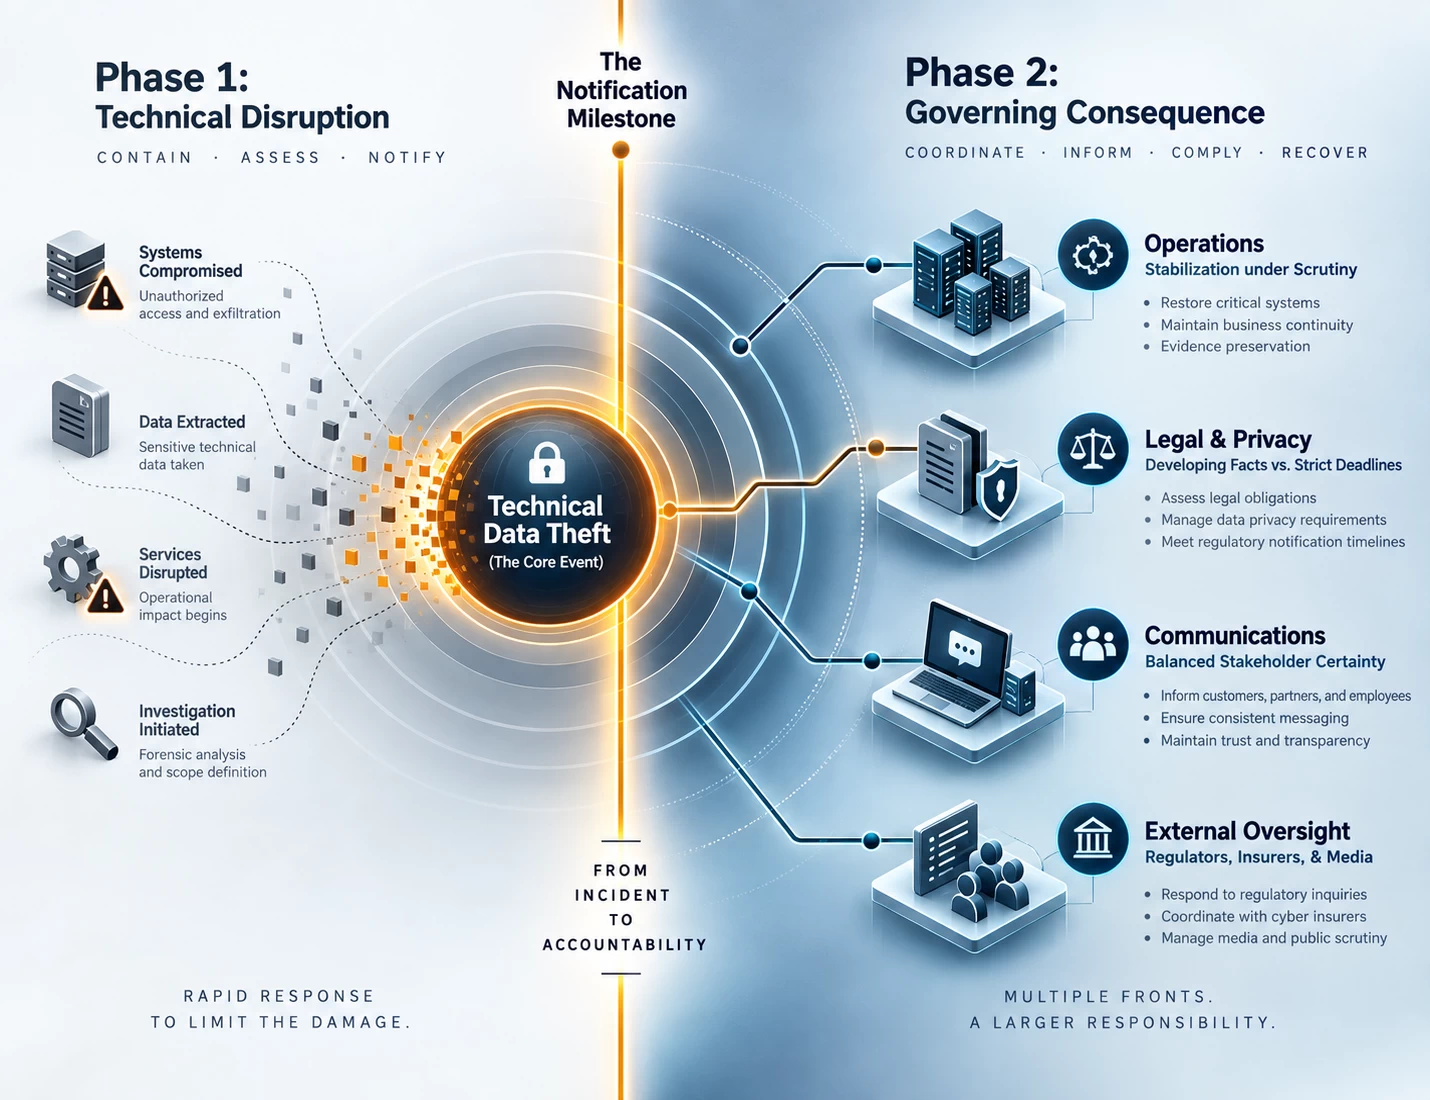
Once data has left, your organisation must stabilise operations while legal, privacy, communications and customer-support demands accelerate.

  • Legal and privacy teams must establish which information was affected and which notification thresholds apply.
  • Customer, patient or employee communications must explain practical risk without claiming certainty the investigation does not yet support.
  • Support teams need guidance for fraud, identity misuse, document replacement or other foreseeable harm.
  • Your executive team must be able to show what was known, what action was taken and why the response was proportionate.

Notification does not close the event. It begins the phase in which people outside your organisation judge the adequacy of the response.

Executive infographic demonstrating the multi-front governance challenge of data theft. It maps how a core technical data-theft incident ripples outward into simultaneous operational, legal, communication, and regulatory challenges, showing that public notification marks the beginning of a massive secondary governance phase rather than the end of the event.

When exposure becomes public consequence

Data exposure changes who must deal with the incident. Customers, patients, employees, partners and families may face fraud, privacy loss, administrative work or anxiety before your organisation has completed its technical investigation.

At the same time, regulators, insurers, suppliers and the media may require different accounts of what happened and what remains uncertain. Customer-support demand can grow while incident teams are still establishing the affected population and the data involved.

Public consequence therefore starts before technical closure. The quality of the response depends on whether your organisation can contain further movement, establish the facts and support affected people without overstating what it knows.

The real loss is control over what happens next

The deepest consequence of data exposure is not always the data loss itself. It is the loss of control over future consequence. Your organisation cannot reliably retrieve every copy. It cannot govern how the data is reused. It cannot predict which affected person will face fraud, intimidation, embarrassment, financial harm or administrative burden. And it cannot cleanly close the incident while the consequences may still reappear elsewhere.

That is why the data-exposure moment matters so much. It moves the organisation from containment into consequence management. From internal control to external uncertainty. From recovery planning to trust repair.

The real loss is not only data. It is control over the consequences that follow.

Preventing exposure is different from managing its consequences

When data is being accessed, staged or transferred, the immediate objective is to interrupt the activity before the exposure becomes larger or irreversible. That requires more than another alert. Your teams need a way to restrict the account, session, server or route carrying the movement.

After exposure, the work changes. Your organisation may need to notify, investigate, support affected people, answer regulators and manage extortion or public disclosure. Those actions can reduce harm, but they cannot retrieve every copy or prove how the information will be used later.

Earlier containment can prevent consequences that later communication and remediation can only manage.

What changes the outcome

If data movement is interrupted early
The consequence can change
If data movement is interrupted early:
Extortion pressure is reduced
The consequence can change:
The attacker has less leverage over public exposure.
If data movement is interrupted early:
Legal and regulatory exposure may narrow
The consequence can change:
Fewer affected records usually means fewer external consequences to manage.
If data movement is interrupted early:
Individual harm is prevented
The consequence can change:
People are less likely to face fraud, exposure or long-term administrative burden.
If data movement is interrupted early:
Your response retains more options
The consequence can change:
A smaller affected dataset and a contained transfer path make the external response more precise and defensible.
The best time to change the outcome is before exposure becomes irreversible.

Where our platform fits

Our platform operates while malicious behaviour is active. It complements your existing security stack by helping authorised teams restrict harmful activity before more data, systems or services are affected.

Ransomware Containment is the platform. Server Intrusion Protection and Virtual Server Protection are additional features that extend protection to compromised administrative access and supported virtual infrastructure.

DETECT
Recognise malicious behaviour and abnormal access before data movement escalates into external consequences.

CONTAIN
Interrupt lateral spread, ransomware encryption, and data movement while the organisation still retains the room to act.

STABILISE
Preserve operational continuity, evidence, and governability while leadership, legal, and operational decisions continue to unfold.

The objective is to interrupt the part of the incident that can still be prevented before your organisation is left managing consequences it cannot reverse.

Run a ransomware resilience assessment

Compare controlled file-encryption scenarios with your existing security controls active, first without Ransomware Containment enabled and then with it enabled. The assessment tests whether active encryption can be isolated before it spreads further.

It does not test data theft or exfiltration, exposure pathways, Server Intrusion Protection, Virtual Server Protection, legal readiness, governance or support for affected people. But, during the assessment session, we can walk your team through the wider containment layer. Alongside the assessment results, we can explain how our platform and its additional Server Intrusion Protection and Virtual Server Protection features, helps detect and interrupt lateral movement, reduce the risk of data theft, protect remote server access and defend virtual environments such as VMware and Hyper-V.

That makes this session useful not only as a ransomware-containment test, but also as a practical discussion about what your organisation can still control when identity, privilege and infrastructure trust come under pressure.

Further readings