Newsletter #8
Published: 14 October 2026
By Stan van Gemert | S10 Group
Series #2: The Governable Organisation
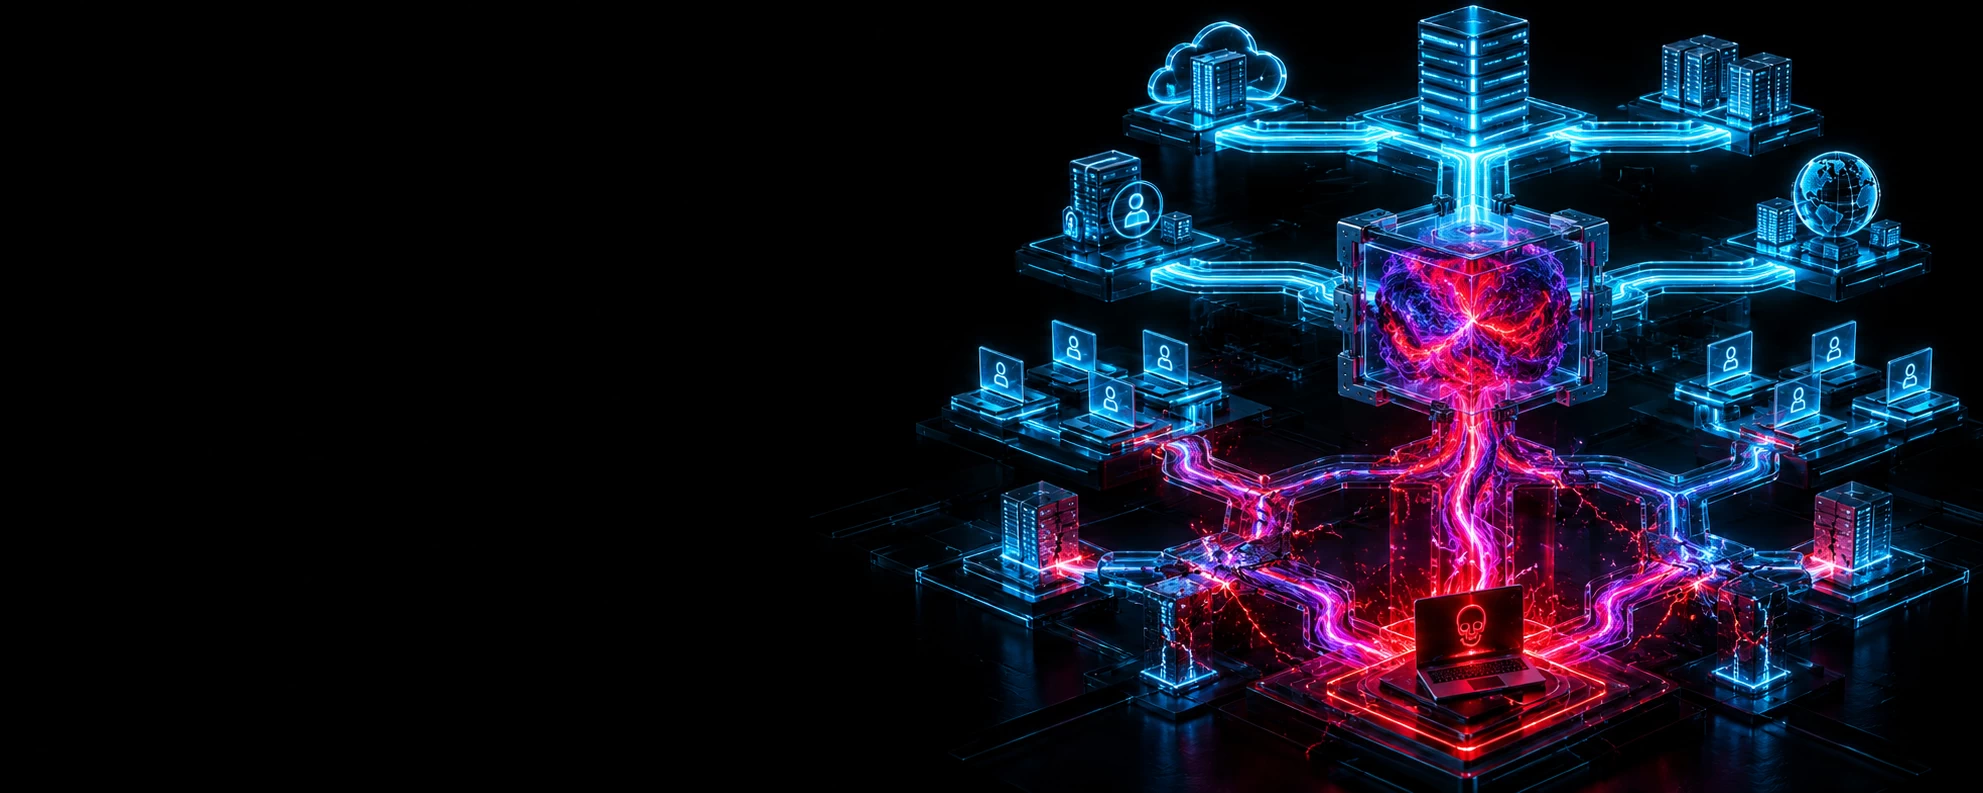
A cyberattack does not always have to break through another barrier to reach the next system. Once an attacker takes over an administrator account or a supplier session, some of the necessary access may already be there. A supplier needs to maintain a service, an administrator needs to resolve a problem and an application needs to exchange data. Those are sound business reasons for granting access. The difficulty begins when access granted for legitimate work remains available after signs of compromise emerge.
Microsoft’s Digital Defense Report 2026 describes identity security as spanning people, applications and agents, and recommends stronger privileged-access enforcement. Its report also examines how AI expands access to sensitive data. The implication for this newsletter is to review the permissions attached to automation alongside those granted to people.
Black Kite’s 2026 Third-Party Breach Report presents an analysis of 136 verified third-party breach events. Its downstream-victim figure describes the incidents it studied, rather than predicting the outcome of every supplier breach. The report provides useful context on how shared dependencies distribute consequences across customer organisations.
Sources:
Microsoft - Microsoft Digital Defense Report 2026
Black Kite - Third-Party Breach Report 2026
https://blackkite.com/reports/third-party-breach-report-2026
Ahold Delhaize’s 13 October statement described its investigation and controlled relaunch. It said there was no indication at that time that customer or associate data had been taken; that remains a dated statement from an ongoing investigation.
CERT-FR confirmed numerous compromises of remote refrigeration controllers. Its guidance includes removing internet exposure, checking configurations and restoring access through a secured VPN or protected network. It warns that resetting vulnerable equipment while leaving it exposed can lead to renewed compromise. Equipment recovery therefore also requires attention to the connection through which it is managed.
Sources:
Ahold Delhaize - cybersecurity update dated 13 October 2026
https://newsroom.aholddelhaize.com/update-on-ahold-delhaizes-cybersecurity-incident/
CERT-FR - refrigeration-controller alert updated 13 October 2026
A suspect supplier session may still be doing useful work. Closing it could remove access to a specialist who is needed to maintain a service. An administrator account may support routine changes as well as the activity under investigation. Those dependencies explain why restricting access can become a difficult operational decision.
I would be concerned if the difficulty only became visible during the incident. A team may know how to terminate a session but have no workable alternative for the service it supports. Another may have an alternative but lack authority to use it. The account remains active while the organisation works out what will happen if it is closed.
Keeping a connection open is also a decision. Its consequences depend on what the account can reach and what the attacker is already doing through it. Your teams need enough understanding of the dependency to compare the disruption of restricting access with the additional damage that continued access could allow.
For me, the practical standard is that trust must be narrowable, interruptible and recoverable. Each word describes a different action, and each deserves a specific answer for the account or connection involved.
Narrowable means reducing what the connection can reach. A supplier may still need access to one system while access to other sites or administrative functions is suspended. Your organisation needs to know whether that separation is technically possible and whether the supplier can continue the necessary work within it.
Interruptible means being able to stop a harmful session or activity with its service effects understood. The responsible team needs an available mechanism, authority to use it and a plan for the work that will be interrupted. Some situations require a broader shutdown, but that should follow from the incident and its consequences rather than from having no more precise option.
Recoverable means agreeing how access can be restored safely. Reconnecting a service, replacing compromised credentials and checking the integrity of the affected environment are related tasks, but completing one does not automatically complete the others. Demand for the service may return before the conditions for restoring its access have been met.
I would begin with an hour around one consequential connection, rather than trying to review the entire environment in one meeting. Choose an administrator account, supplier session or management console whose compromise could affect an essential service. Bring together the people who understand its access and the people who depend on its work.
Use the first ten minutes to map what it can reach. Spend fifteen minutes agreeing what signs of misuse would justify a restriction, then fifteen walking through the first action and its likely service impact. Use the next fifteen to define the conditions for reconnection, and the final five to assign unresolved dependencies to named owners.
The discussion should produce a specific next step. If the team assumes a session can be terminated, arrange an appropriately scoped technical check. If the service cannot continue without that session, work through the operating alternative. The discussion identifies what needs validation; it does not by itself validate the technical response or the wider continuity plan.
Our Ransomware Containment platform provides a defined intervention when illegitimate file encryption begins. It agentlessly monitors file activity across the protected data environment and isolates the responsible user, session or device, helping prevent encryption from spreading further through protected data.
Additional Server Intrusion Protection (SIP) and Virtual Server Protection (VSP) features run on that platform. SIP extends protection to compromised server access, while VSP addresses attacks directed at supported hypervisor environments.
These capabilities give incident and infrastructure teams ways to contain specific harmful activity while the wider investigation and operational response continue.
The broader questions in this newsletter still require work across access management, supplier relationships and operational planning. Our platform does not make every connection narrowable or decide when equipment can safely be disconnected. Those decisions need the responsible teams and an understanding of the services involved.
A long list of approved accounts and suppliers tells you who was granted access. The more useful conversation for this issue is what one compromised connection could reach, what essential work depends on it and how that access could be changed while an incident is developing.
In the next issue, "The First Hours Are No Longer Internal", I will look at what happens when customers, regulators and other stakeholders need explanations while the investigation is still developing. Before that pressure arrives, it is worth finding the connection for which your teams cannot yet answer the question above. I would welcome hearing where that difficulty lies in your organisation.
AP - report on European supermarket cyberattacks dated 13 October 2026
https://apnews.com/article/78a813a8efd466b360655339f96083dc
FDA - medical device cybersecurity guidance and resources
https://www.fda.gov/medical-devices/digital-health-center-excellence/cybersecurity
Dutch Parliament - summary of questions on the nationwide Albert Heijn disruption, dated 13 October 2026
Lemonde - A disastrous day for French supermarkets after massive cyberattack targets refrigeration systems
https://www.lemonde.fr/en/economy/article/2026/10/13/a-disastrous-day-for-french-supermarkets-after-massive-cyberattack-targets-refrigeration-systems_6758535_19.html?utm_source=chatgpt.com
Unit 42 - case study on third-party-managed gateway access at a European bank, dated 13 October 2026
https://unit42.paloaltonetworks.com/noise-inside-network-third-party-risk/
This case is useful context for the newsletter because it shows how compromised credentials and a supplier-managed gateway can turn trusted access into internal reconnaissance, documentation exposure and attempted expansion of control before further movement is contained.