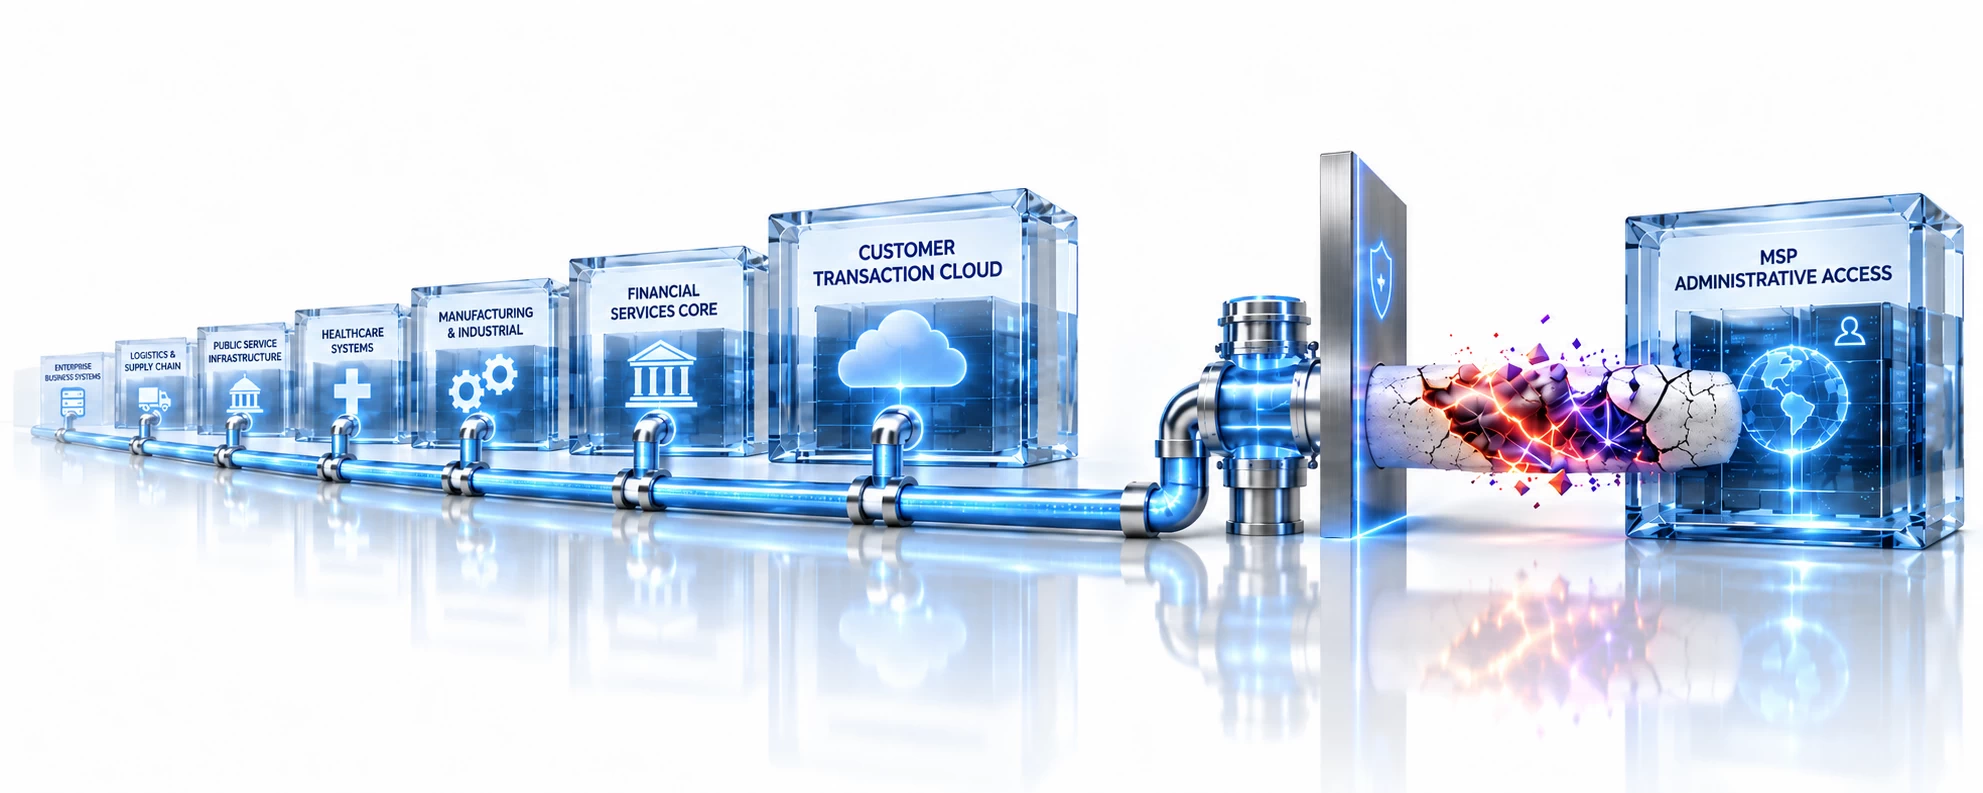
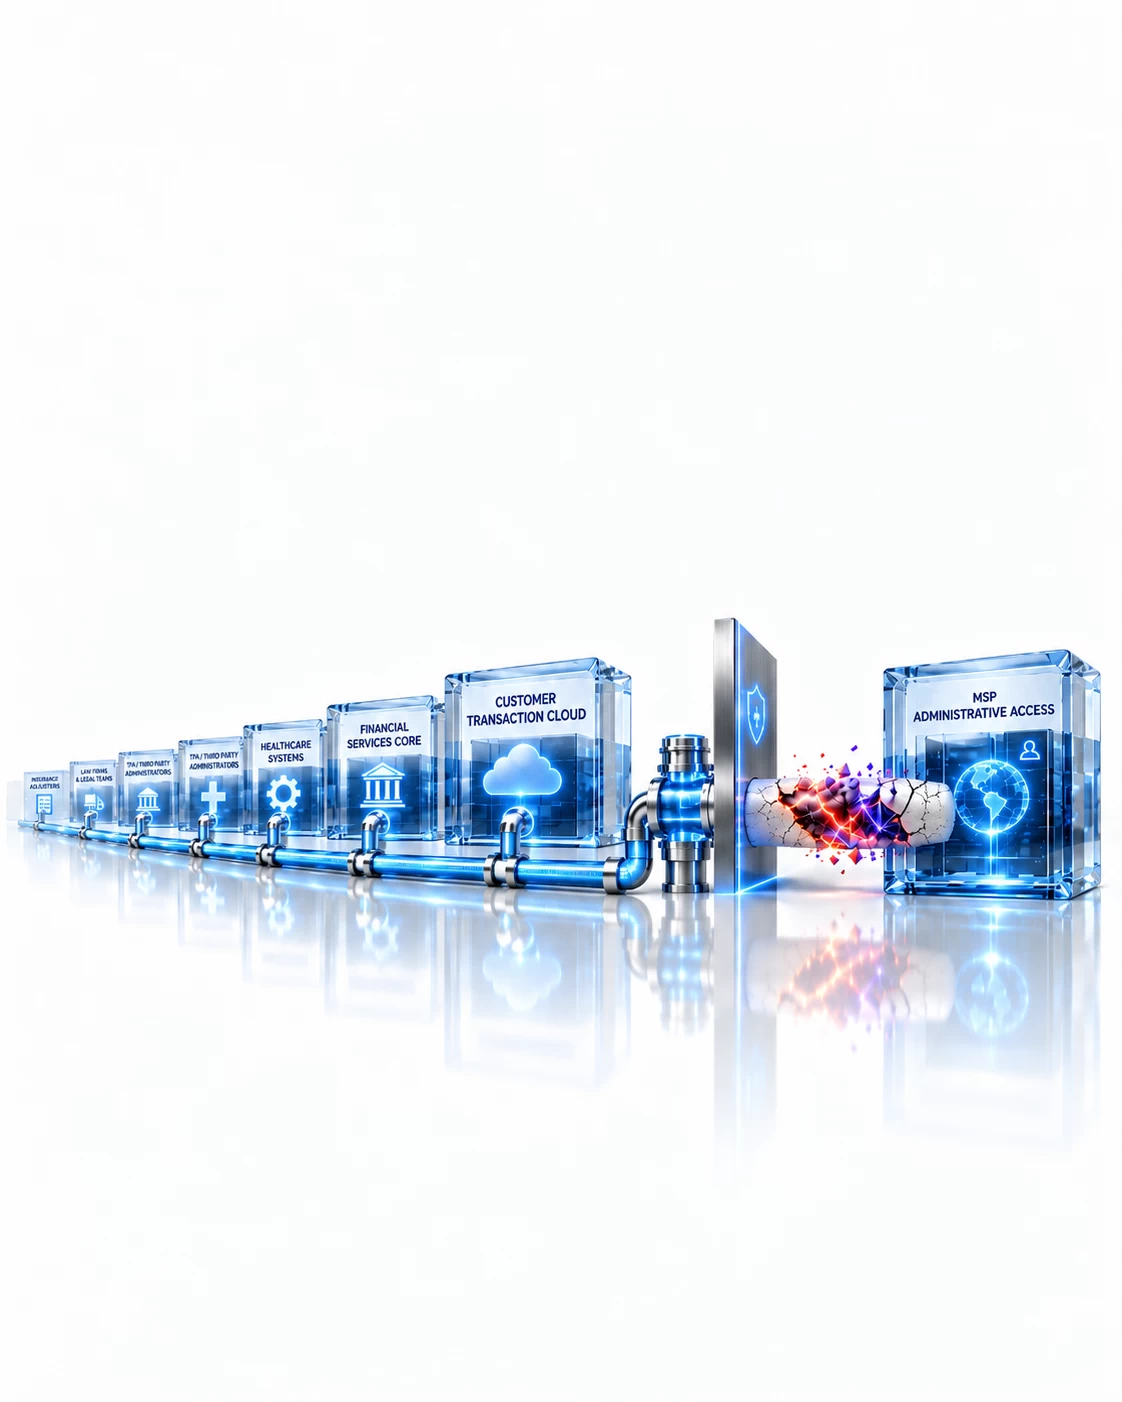
A joint CISA advisory explains why MSP exposure differs from an isolated customer incident. Managed services commonly depend on trusted connectivity and privileged access to customer systems, which can allow a compromised provider or management route to become an entry point into several client environments.
Kaseya confirmed that attackers exploited zero-day vulnerabilities in its on-premises VSA product in July 2021, bypassed authentication and executed ransomware on managed endpoints. Approximately 50 Kaseya customers were breached, but the provider model extended the impact to an estimated 800 to 1,500 downstream businesses.
Swedish supermarket chain Coop experienced the operational consequence through its technology supply chain rather than a direct attack against the retailer. Around 700 of its 800 stores had to close when tills and self-service checkouts stopped working. Incident responders reported that all stores had reopened within six days.
A Dutch incident in April 2021 shows the same concentration risk without the same propagation mechanism. Ransomware encrypted a significant part of Managed IT's infrastructure, leaving 96 notary offices unable to work normally or pass deeds. The first offices regained access several days after the attack and the last clients followed later that week. Managed IT's connected off-site backups had also been encrypted, although investigators reported no indication that client data had been stolen.
Neither case means that every MSP incident will spread into every client environment or cause permanent data loss. Together they show why provider resilience cannot be judged only by whether backups exist or whether the original target was the MSP. One event can create simultaneous client interruption, a shared recovery workload and urgent demands for evidence before the full technical picture is available.
Recent reporting from ConnectWise and Huntress shows how provider compromise continues to evolve through abused identities, remote access, RMM tooling, mailbox manipulation and authenticated-session takeover. The lasting issue is concentrated authority: when legitimate provider access begins carrying unsafe behaviour, your teams need a containment boundary before consequences multiply across clients.
Sources:
CISA - Protecting Against Cyber Threats to Managed Service Providers and their Customers
https://www.cisa.gov/news-events/cybersecurity-advisories/aa22-131a
Kaseya - Incident Overview & Technical Details
https://helpdesk.kaseya.com/hc/en-gb/articles/4403584098961-Incident-Overview-Technical-Details
Kaseya - Kaseya Responds Swiftly to Sophisticated Cyberattack
https://www.kaseya.com/press-release/kaseya-responds-swiftly-to-sophisticated-cyberattack-mitigating-global-disruption-to-customers/
Truesec - Back in Business After the Largest Ransomware Attack of All Time
https://www.truesec.com/cases/back-in-business-after-the-largest-ransomware-attack-of-all-time
NOS - Nearly 100 Notaries Unable to Execute Deeds Following IT Vendor Hack
https://nos.nl/artikel/2377387-bijna-honderd-notarissen-kunnen-geen-akten-passeren-na-hack-bij-ict-leverancier
KNB - Breached: What Now?
https://www.knb.nl/actueel/notariaat-magazine/2021/notariaat-magazine-nr-4-juni-2021/gehackt/
Tweakers - IT Firm Managed IT Encrypted via BitLocker; Ransom Has Been Paid
https://tweakers.net/nieuws/180794/data-ict-bedrijf-managed-it-was-versleuteld-met-bitlocker-en-losgeld-is-betaald.html
Connectwise - 2026 MSP Threat Report
https://www.connectwise.com/resources/msp-threat-report
Huntress - The Huntress Tragic Quadrant: Beat the Hype on Cyber Tactics Wrecking Businesses
https://www.huntress.com/blog/huntress-tragic-quadrant-cyber-threats