Three marble security pillars support a dark titanium risk sphere, stabilised by a blue-edged sapphire containment plane.Three marble security pillars support a dark titanium risk sphere, stabilised by a blue-edged sapphire containment plane.
Part of Cybersecurity Blind Spots

Firewall, Antivirus and Backup Are Necessary.
They Are Not Enough.

Why the presence of security controls needs to be matched by evidence of what they can do.

The distance between installed controls and an active capability

“We have a firewall, antivirus and backups” is a reasonable starting point for a cybersecurity discussion. Those investments help reduce exposure, prevent and detect threats, and restore affected systems. They remain essential when your organisation prepares for ransomware or another serious intrusion.

The statement becomes less useful when it is offered as the complete answer. It does not tell the executive team which connections an attacker could use after compromising an account, what an endpoint tool would stop, or whether an essential service could be restored from the available copies.

Each of those questions needs evidence about coverage, configuration and the result of a defined test. A list of installed controls describes your investment; the next step is to establish the capabilities that investment has delivered.
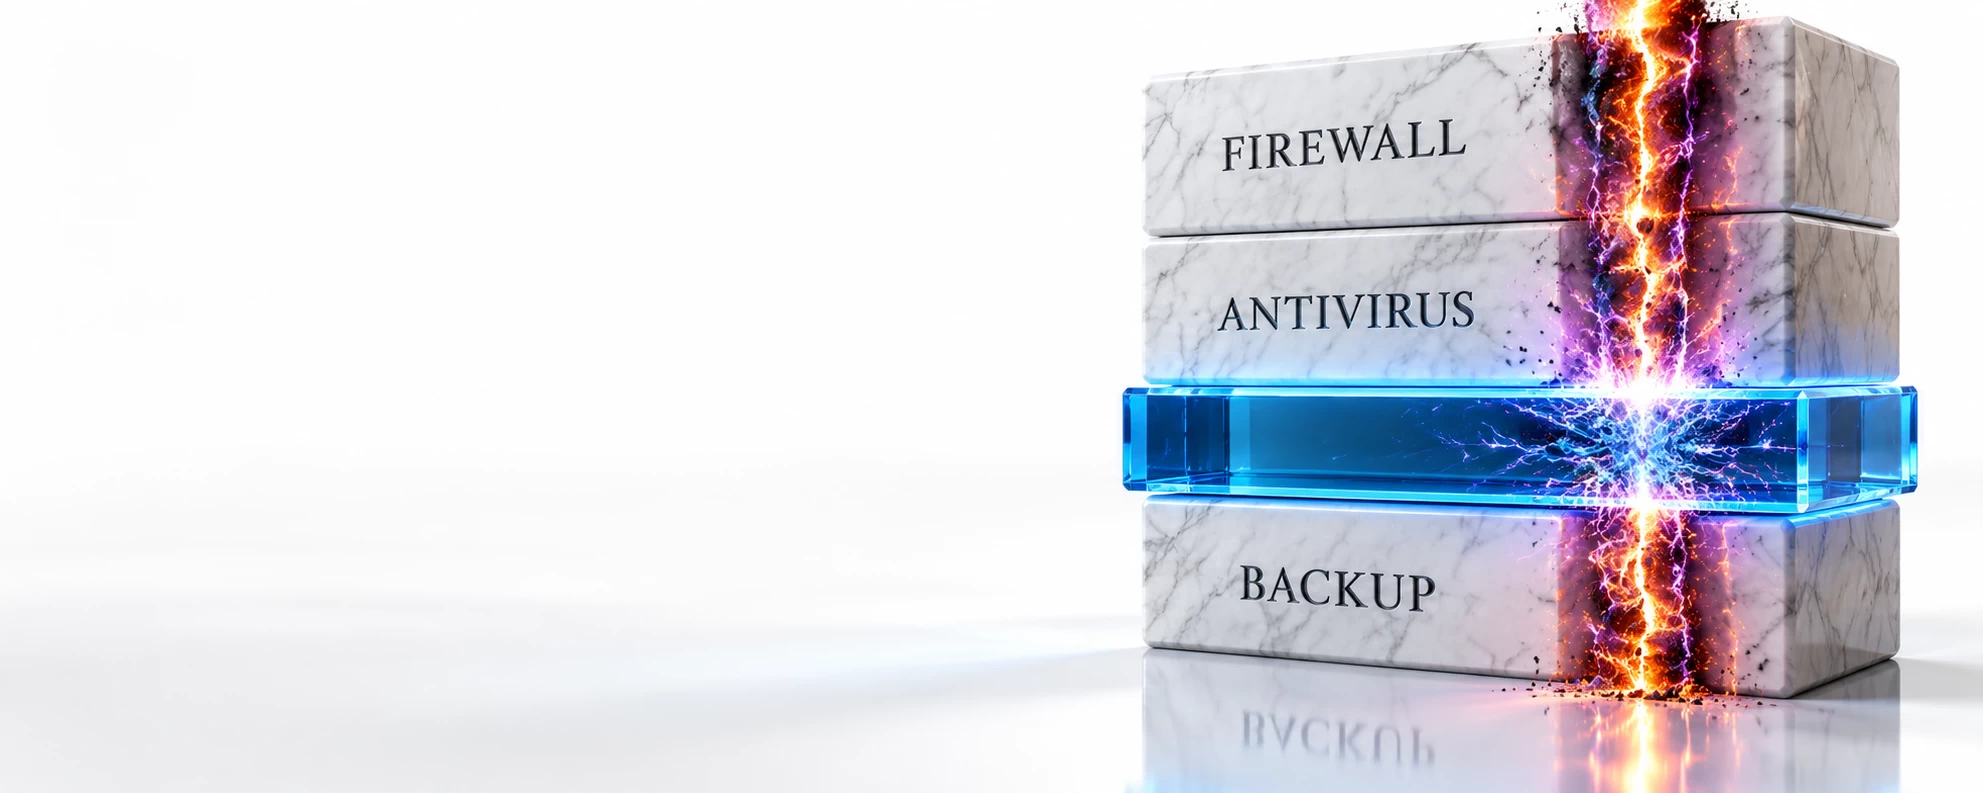
Having a control in place and demonstrating its effect in a specific incident scenario are different forms of evidence.
The decision is how much assurance each supports.

Why the three pillars became the familiar answer

Firewall, antivirus and backup gave boards and IT teams a practical way to organise security spending: restrict access, prevent harmful activity and retain a way to restore what was lost. They also provided visible evidence that important responsibilities had been addressed.

The problem arises when the existence of those provisions ends the enquiry. A deployed firewall may have broad exceptions for administrators or suppliers. An endpoint tool may cover most workstations but have different capabilities on servers. A backup service may report successful jobs without a recent restoration of the business service that depends on them.

Those are questions about the way your environment is operated. Answering them can confirm that existing measures work, expose a configuration gap or identify a capability that needs to be added. The purpose is to find the actual boundary of protection.

Why valid access changes the enquiry

A ransomware intrusion can begin with a compromised account or session, followed by the misuse of tools already available to an administrator. The activity may cross an approved connection and run through a legitimate application even though the person directing it has no authority to do so.

Valid access needs a tested boundary

Paloalto Unit 42 - Global Incident Response Report 2026
‍
Identity - based entry in investigated cases
The 2026 Global Incident Response Report attributes 65% of initial access to identity-based techniques. Its case data covers more than 750 incidents handled between October 2024 and September 2025. Include credential misuse and social engineering when choosing scenarios for your own controls.
https://www.paloaltonetworks.com/resources/research/unit-42-incident-response-report

Palo Alto Networks - VM-Series
Firewalls can protect internal traffic
Its Cisco ACI deployment guidance describes a firewall configuration for east-west traffic. Internal protection is possible; the relevant question is where it has been deployed and what the rules permit.
https://docs.paloaltonetworks.com/vm-series/deployment/private-cloud/set-up-a-firewall-in-cisco-aci/integrate-the-firewall-with-cisco-aci-in-network-policy-mode/deploy-the-firewall-to-secure-east-west-traffic-in-cisco-aci

Microsoft Ignite - Take response actions on a device
‍Endpoint protection can include response
Defender for Endpoint documentation includes device isolation and other response actions. A review should establish the supported assets, enabled capability and observed result.
https://learn.microsoft.com/en-us/defender-endpoint/respond-machine-alerts

What these public sources mean for your organisation
Follow a compromised account through a defined scenario and identify which deployed measure blocks, detects or restricts the activity. A product category alone does not describe the boundary in your environment.

View more details chevron A white downward-facing V-shaped chevron on a transparent background.
View more details
Close more details

The practical question is what your current measures would do with that access. An accepted login might still be constrained by internal network rules, limited permissions or endpoint protection. Where those safeguards are missing, bypassed or excluded, the same account may be able to reach additional servers or sensitive repositories.

Your review therefore needs to follow the permitted action far enough to identify where it would be blocked, detected or interrupted. Successful authentication alone cannot answer that question.

What a firewall establishes

A firewall can enforce rules about traffic entering, leaving or moving between parts of your environment. Depending on its deployment and configuration, it can inspect internal traffic and help limit movement between systems as well as protect the external boundary.

The presence of a firewall does not establish which of those functions is being applied to a particular connection. An administrative or supplier route may be deliberately allowed because an important service depends on it. If the account using that route is compromised, the incident team needs to know which restrictions still apply and which further destinations remain reachable.

The useful evidence is the relevant rule, the systems it covers and an observed result. For example, can a compromised support account connect from its approved server to a backup management console? If the answer is no, the test should show the restriction working. If the answer is yes, your team can examine whether that access is required and how it is constrained.

What antivirus and EDR establish

Antivirus and endpoint detection and response tools can do more than recognise known malicious files. Depending on the product, supported system and configuration, they can detect suspicious behaviour, block execution, quarantine files or isolate devices. Existing endpoint response capability deserves to be established as part of the assessment of your environment.

A licence or deployment record, however, does not show that every relevant server is covered, that the right response is enabled or that it can operate through the access path used in a particular attack. The misuse of a legitimate remote-access tool or script also needs to be evaluated in context.

Ask your team to distinguish what was detected from what was stopped. A test record should identify the activity, the affected system, the response and whether that response was automatic or required a person. Where approval was needed, the elapsed time and the available permissions are part of the result.

The question is how the deployed capability behaves in the scenario your organisation needs to handle. The detailed design of an alert-to-action response is a separate enquiry.

What a backup establishes

A completed backup job is evidence that a defined copying process ran. A successful restoration demonstrates more, but only for the data, infrastructure and dependencies included in that exercise. Neither result should be extended beyond its tested scope.

For an essential service, your recovery team needs to establish whether the copies are usable, whether the required accounts and management systems remain available, and whether restoration can meet the operational requirement. An attacker’s access to backup administration is a further condition to examine.

What an audit establishes

Audits and assurance reviews can examine both the existence and the effectiveness of controls. Their value depends on the questions asked, the evidence examined and the scope of the conclusion.

A review of documented policies and installed tools supports a different conclusion from an exercise that observes a compromised account, a containment action and a service restoration. Even a technically thorough review may exclude a supplier connection, a virtual environment or a recovery dependency that matters to your organisation.

Ask which scenarios were evaluated, which systems were excluded and what changed after the findings. That gives the audit a defined role in your evidence base.

Confidence, coverage and a practical exercise

Veeam - Report
Define the recovery result being discussed
Its 2026 Data Trust and Resilience Report surveyed more than 900 senior IT, security and risk respondents. While 90% expressed confidence in recovery within RTOs, 28% of the ransomware-affected subgroup reported recovering all affected data.
https://www.veeam.com/company/press-release/veeam-report-reveals-a-market-wide-shift-from-recovery-confidence-to-proven-data-resilience-amid-ransomware-threats-and-ai-adoption.html
‍

PwC - Cybersecurity is now a boardroom responsibility
An exercise exposed gaps that an inventory missed
PwC describes an unnamed organisation’s joint exercise with defenders and ethical hackers. Some techniques were not detected. Mapping the stack then revealed uncovered techniques and overlapping tools, giving the organisation a basis for a targeted investment discussion.
https://www.pwc.nl/en/topics/blogs/can-you-truly-prove-your-organisation-is-cyber-resilient.html

What these public sources mean for your organisation
Ask for the tested result and the unresolved findings, alongside the control list. A recovery exercise and a detection exercise answer different questions, but both make the scope of assurance more concrete.

View more details chevron A white downward-facing V-shaped chevron on a transparent background.
View more details
Close more details

The next security discussion can start with the three pillars and then ask for a result. A compact evidence review makes the distinction practical:

Control or review
Question to answer
Evidence to request
Control or review
Firewall
Question to answer
Which connections can a compromised account still use?
Evidence to request
A scoped test showing which connections are blocked or allowed, with the relevant rules and logs.
Control or review
Antivirus and EDR
Question to answer
What happens when an attacker uses a legitimate administration tool?
Evidence to request
Detection and response records showing the activity, the action taken and the systems covered.
Control or review
Backup
Question to answer
Can an essential service be restored using the available copies and dependencies?
Evidence to request
A restoration result recording data completeness, elapsed time and the accounts and infrastructure required.
Control or review
Audit and assurance
Question to answer
Which incident capabilities were actually examined?
Evidence to request
The review scope, test methods, findings and unresolved limitations, linked to the services that matter.

Every result needs a date, a defined scope and an owner for any unresolved finding. Changes to access, infrastructure or response settings may also change what the earlier test establishes. A useful assurance programme keeps that evidence current enough to support the next decision.

The same discipline applies to broader questions about lateral movement, data theft and continuity. Select the capability to be examined and agree a suitable validation method. A file-encryption test cannot demonstrate all of them.

How our platform contributes to containment

Our contribution is to add specific containment capabilities alongside your existing measures. Ransomware Containment is our platform: it agentlessly monitors file activity in the protected data environment and isolates the responsible user, session or device when illegitimate encryption begins.

Additional Server Intrusion Protection (SIP) and Virtual Server Protection (VSP) features run on the platform. SIP detects and contains compromised server access, while VSP protects supported hypervisor environments against attacks directed at that layer. Their relevance depends on the systems and attack activity your organisation needs to address.

For your team, the decision starts with the requirement and the evidence already available. Where active encryption remains a concern, the assessment can show the effect of RC within an agreed test scope. Server intrusion, virtual infrastructure, data-exfiltration risks and recovery dependencies need their own technical discussion and appropriately scoped validation.

Compare the response to active encryption

Our remote ransomware resilience assessment examines one defined capability. In an agreed, isolated test environment, we run controlled file-encryption scenarios with your existing security controls left active, first without Ransomware Containment enabled and then with it enabled.

The comparison provides an observable result for active encryption within that scope. During the session, we can explain the additional features like lateral-movement interruption, data-exfiltration prevention, and discuss broader requirements separately.

The question to take into the next review

Firewall, antivirus and backup belong in the security model. The assurance you draw from them should be matched to what they have actually demonstrated.

For each capability on which an essential service depends, can your team show the scope, the observed outcome and the action required where the evidence is still missing?

Further readings