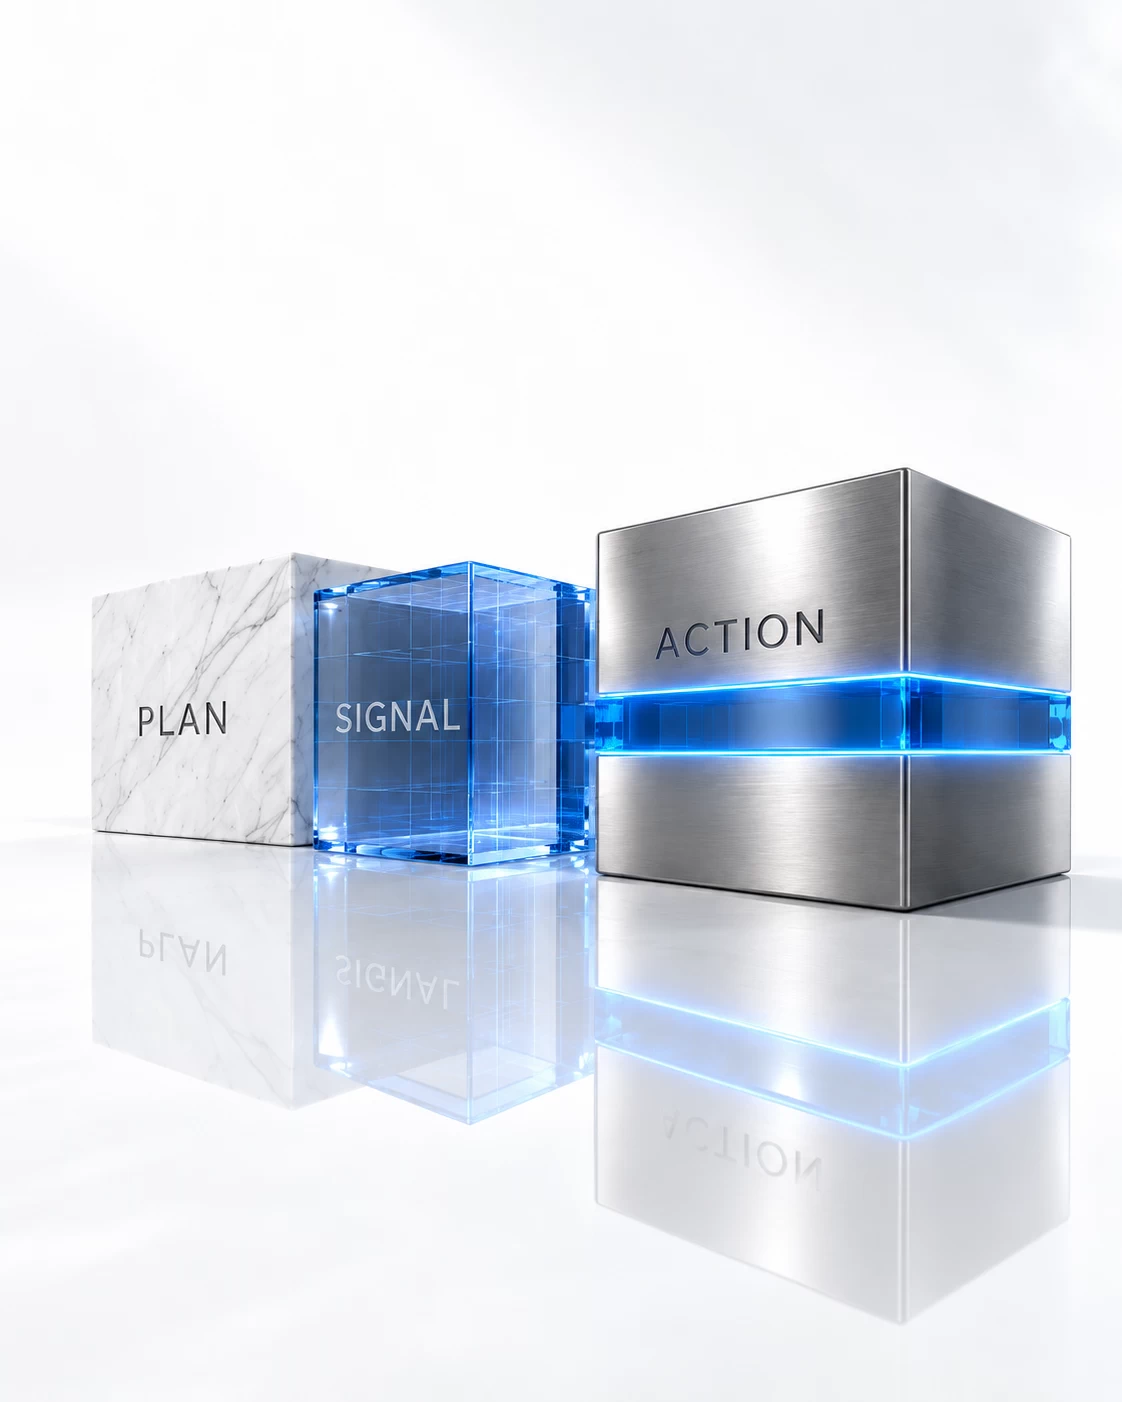
Plan, Signal and Action blocks with a blue containment band illustrating cyber incident readiness.Plan, Signal and Action blocks with a blue containment band illustrating cyber incident readiness.
S10 Group Article series · Why resilience changed

When Prepared
Does Not Mean Ready

Why preparedness becomes readiness only
when your organisation can execute a bounded move under pressure
Article #18
Published: 12 October 2026
By Stan van Gemert | S10 Group
By Stan van Gemert
Why resilience changed series
Executive summary

The previous publication, "The Missing Budget Line Between Prevention and Recovery", made the investment case for containment during an active incident. Funding that capability creates an option; it does not establish that your organisation can use the option when it matters.

"When Prepared Does Not Mean Ready" examines the gap between arrangements made in advance and a response your teams can carry through. A credible alert may arrive while services still run, evidence remains incomplete and the usual approver cannot be reached. Readiness depends on connecting the signal to a proportionate decision, working access, an understood service consequence and evidence of the result. Preventive security remains essential, but plans, contracts and exercises need to be tested against the decisions they are intended to support.

The next publication, "The Goal Is Not Perfect Prevention", defines the operating outcome that readiness should protect: an essential service your organisation can sustain safely within known limits after normal operation is disrupted.

Everything was prepared except the first move

Consider a familiar incident-room pattern at 22:07 on a Friday. A credible alert shows a valid administrative session behaving in a way it should not. Nothing is visibly encrypted, and core services are still running. The activity is moving through a connection your organisation normally trusts.

The security lead recommends pausing the route. Operations asks which services will stop with it. Legal asks how strong the evidence is. The incident plan names the right roles, the external retainer is in place and the last tabletop exercise was completed. The executive who can accept the operational disruption is not answering.

Your organisation has prepared for an incident, but it has not yet made this decision executable.

Prevention, planning and exercises remain valuable. The gap appears when their existence is treated as proof that your teams can still act after a trusted route becomes unsafe and the operating picture is incomplete.

Preparation is not readiness until control can be exercised.

The firewall did not fail

Sometimes the firewall does exactly what it was designed to do. It sees no forbidden connection because the intruder is using a valid credential, an inherited token, a supplier route or a trusted integration. The pathway is permitted. The behaviour is not.

Strong authentication, secure configuration, monitoring, segmentation and disciplined supplier access still reduce the probability and reach of compromise. They also give responders more useful boundaries once something is wrong.

After a trusted route has been misused, the decisive question widens. Your teams need to narrow access, interrupt harmful activity and protect essential operations before the incident reaches further.

Prevention reduces the likelihood and reach of compromise.
Your teams still need a usable response after entry.

Why prepared does not mean ready

Preparedness describes what your organisation has arranged before pressure arrives: policies, playbooks, technical controls, backups, contracts, contact lists, exercises and reporting. These are necessary assets that create response options.

Readiness describes whether those options still connect when the situation is live. Can a credible signal reach the person who can decide? Can that person authorise a limited action? Can your teams execute it with the access available? Can essential services tolerate the resulting degraded state? Can the responsible executive record why the move was proportionate and what would justify reversing it?

A plan can answer each question in a different section and still fail to join them into one operating move. That is why maturity on paper and hesitation in practice can coexist without contradiction.

The readiness gap is not the absence of documents. It is the distance between a recognised condition and an executable response.

When the intruder logs in

The Change Healthcare attack provides a narrow public example of how one trusted path can change the problem. In written answers to the US Senate Finance Committee, UnitedHealth Group chief executive Andrew Witty stated that criminals used compromised credentials to access a Change Healthcare Citrix portal that did not have multifactor authentication.

That fact establishes a specific access failure. It does not prove that the wider organisation lacked a security programme, and it does not mean one preventive control would have answered every later decision. Its value here is more limited: a large control estate can be bypassed through one permitted route, after which the operating question becomes what access can be removed, what activity can be contained and what services must be protected while the picture is still incomplete.

The same pattern can appear through a supplier session, cloud identity, developer token or remote-management pathway. The technical route changes. The readiness test does not.

What the public evidence supports

NIST SP 800 61 Revision 3
Incident response is integrated across cyber-risk management. Govern, Identify and Protect support preparation; Detect, Respond and Recover address discovering, managing, containing and recovering from incidents. Preparation and live response are related, but they are distinct activities.
https://csrc.nist.gov/pubs/sp/800/61/r3/final

NCSC Board Toolkit and Exercise in a Box
Response plans should define severity, decision authority and responsibilities, then be practised. Exercising helps your teams examine procedures and decision mechanisms and identify improvements before a real event.
https://www.ncsc.gov.uk/collection/board-toolkit/principle-d-incident-planning-response-recovery/planning-your-response-to-cyber-incidents
https://www.ncsc.gov.uk/section/exercise-in-a-box/overview

Change Healthcare Senate record
UnitedHealth Group’s written response states that compromised credentials were used to access a Citrix portal without multifactor authentication. The record establishes a specific access path, rather than a complete readiness score for the organisation.
https://www.finance.senate.gov/download/responses-for-questions-for-the-record-to-andrew-witty

These sources support the preparation and execution distinction and one documented access fact. They do not establish the result of an unreported incident decision.
View more details chevron A white downward-facing V-shaped chevron on a transparent background.
View more details
Close more details

Readiness reveals itself in a bounded move

Readiness is often discussed as a broad condition: your organisation is ready or it is not. Under pressure, it is more useful to test a specific move. Where appropriate, that may mean temporarily suspending one supplier connection, revoking a privileged session, isolating a segment or narrowing a high-risk data flow while essential operations continue elsewhere.

For that move to be real, six things have to connect:

  1. Trigger: a defined condition strong enough to justify action, even when the full incident is not yet known;
  2. Authority: a named decision owner, an alternate and an agreed limit to what they may authorise;
  3. Access: working credentials, clean communications and the practical means to execute when normal administration may be unsafe;
  4. Containment option: a move narrow enough to reduce attacker freedom without treating the whole organisation as one switch;
  5. Degraded operation: an understood way for essential services to continue, slow down or fail safely while the boundary holds; and
  6. Evidence and return criteria: a record of what changed, why it changed and what must be true before access or service is restored.

These six elements provide a way to examine one response, rather than a universal incident playbook. An untested dependency on someone’s availability or an uncertain approval chain can leave an otherwise useful capability difficult to execute.

A credible signal needs a practised route into proportionate action when the evidence warrants it.

Exercises need to expose the execution gap

Tabletop exercises are valuable because they create a safe place to expose assumptions. They become less useful when success is defined by reaching the end of the scenario, producing a list of actions or confirming that everyone knew their role.

An exercise can follow one decision through its operational handoffs. Can the right person authorise the supplier restriction? Is an administrator reachable? Does the alternative communication channel work? Has the operational consequence been understood? A separate, appropriately scoped technical test is needed to demonstrate that the restriction itself takes effect. Discussion alone cannot establish that result.

The purpose is not to surprise people for sport. It is to find the point where an assumed capability turns into delay. That is where the next improvement belongs.

The sector changes the operating consequence

In healthcare, a containment decision may have to isolate an unsafe route without losing the local information needed for care. In finance, it may have to narrow a trusted connection while essential transactions continue under additional control. In manufacturing, it may have to separate corporate identity or remote support from plant operations without creating a new safety risk.

The technical design and acceptable degraded state will differ. The executive task is to decide in advance which boundary can move, who may move it and how essential work will continue within the restriction.

That is why readiness cannot be inferred from expenditure or the number of controls deployed. It has to be demonstrated against the dependencies that make action difficult.

What your executive team should pressure test

Before the next incident, a board or executive team does not need to approve every technical response. It does need evidence that the organisation has converted preparation into executable control.

  • Which bounded containment moves have already been accepted for the highest-consequence scenarios?
  • What observable conditions allow those moves before full certainty exists?
  • Who can decide out of hours, and what happens if the primary owner is unavailable or affected?
  • Which essential operations can continue in a controlled degraded state after the move?
  • What evidence will the executive team receive to confirm the action worked and to support a safe return?

These are readiness questions, not demands for a perfect forecast. They make uncertainty governable by deciding what can be done without pretending the organisation will know everything first.

Which control move has already been accepted before pressure arrives?
If something slips through, how much control can we actually exercise?

Where our platform fits

Our platform complements preventive security, incident command, identity governance, business continuity, forensic investigation and executive authority. Those capabilities help your organisation recognise the condition, choose a proportionate move and govern its consequences.

Ransomware Containment monitors supported SMB and NFS file activity without endpoint agents and can isolate the responsible user or session when illegitimate active encryption is detected.

Server Intrusion Protection and Virtual Server Protection are additional features for compromised administrator use on servers and supported host-level threats in virtual environments.

The operational value lies in connecting a supported containment action to a defined trigger, clear authority and an understood service consequence.

Ready is a condition, not a feeling

A mature organisation should feel confident in the work it has done. Confidence is useful when it supports action. It becomes dangerous when it substitutes for proof.

Preparedness creates plans, contracts, controls and exercises. Readiness becomes visible when a credible signal reaches a decision owner, a proportionate move can be executed, essential operations remain within safe limits and your executive team can explain the result.

Prevention and preparation remain essential. Your organisation also needs evidence of what remains controllable when a trusted route becomes unsafe.

The next horizon

"The Goal Is Not Perfect Prevention" moves from the ability to act to the service that action must preserve. It asks which essential function can continue, what information and people it needs, and whether its fallback remains usable when a shared dependency has to be restricted.
Hear first when a new S10 Group release is published

Would you like to receive a short note when S10 Group publishes a new article or newsletter?

Leave your name and email address below. We will send a short update when a new release is available, with a brief summary and a direct link to the publication.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

FOCUSED RANSOMWARE RESILIENCE ASSESSMENT

Compare controlled file-encryption scenarios with your existing security controls active, first without Ransomware Containment and then with it. The assessment itself is limited to encryption, but alongside the assessment results, we can explain how our platform and its additional Server Intrusion Protection and Virtual Server Protection features, helps detect and interrupt lateral movement, reduce the risk of data theft, protect remote server access and defend virtual environments such as VMware and Hyper-V. That makes the session useful not only as a ransomware-containment test, but also as a practical discussion about what your organisation can still control when identity, privilege and infrastructure trust come under pressure.‍
Bright conceptual visual of frosted-glass blocks where the first block is stopped by a titanium pillar, representing ransomware containment before wider operational disruption spreads.

Coming soon

Wednesday 14 October, Leadership-series #7: "The Goal Is Not Perfect Prevention."

Friday 16 October, Operational Attack-series #7: "The Foundation Failed While the Building Still Stood."

Further readings