Article #36 (extra edition: malvertising)
Published: 16 November 2026
By Stan van Gemert | S10 Group
By Stan van Gemert
Special edition series
The previous publication, “When Reality Overtakes Preparation”, examined how your teams adapt an incident response when several assumptions in the plan fail at once.
In this special edition, we examine a compromised advertising tag on Dutch publisher sites. This tag sent technical visitor data to an attacker’s server and attempted to exploit certain unpatched iPhones. A separate infection reported by iVerify shows why the risk extends to employers when a device carries work credentials. For CIOs, CISOs and owners of digital services, the decisions are practical. Establish what ran in the browser, withdraw exposed work access and be ready to interrupt malicious activity if stolen credentials reach protected infrastructure.
The next publication, “The Organisation Itself Becomes The Bottleneck”, examines why a credible containment recommendation can stall while your teams work out who can authorise it and which services it would interrupt.
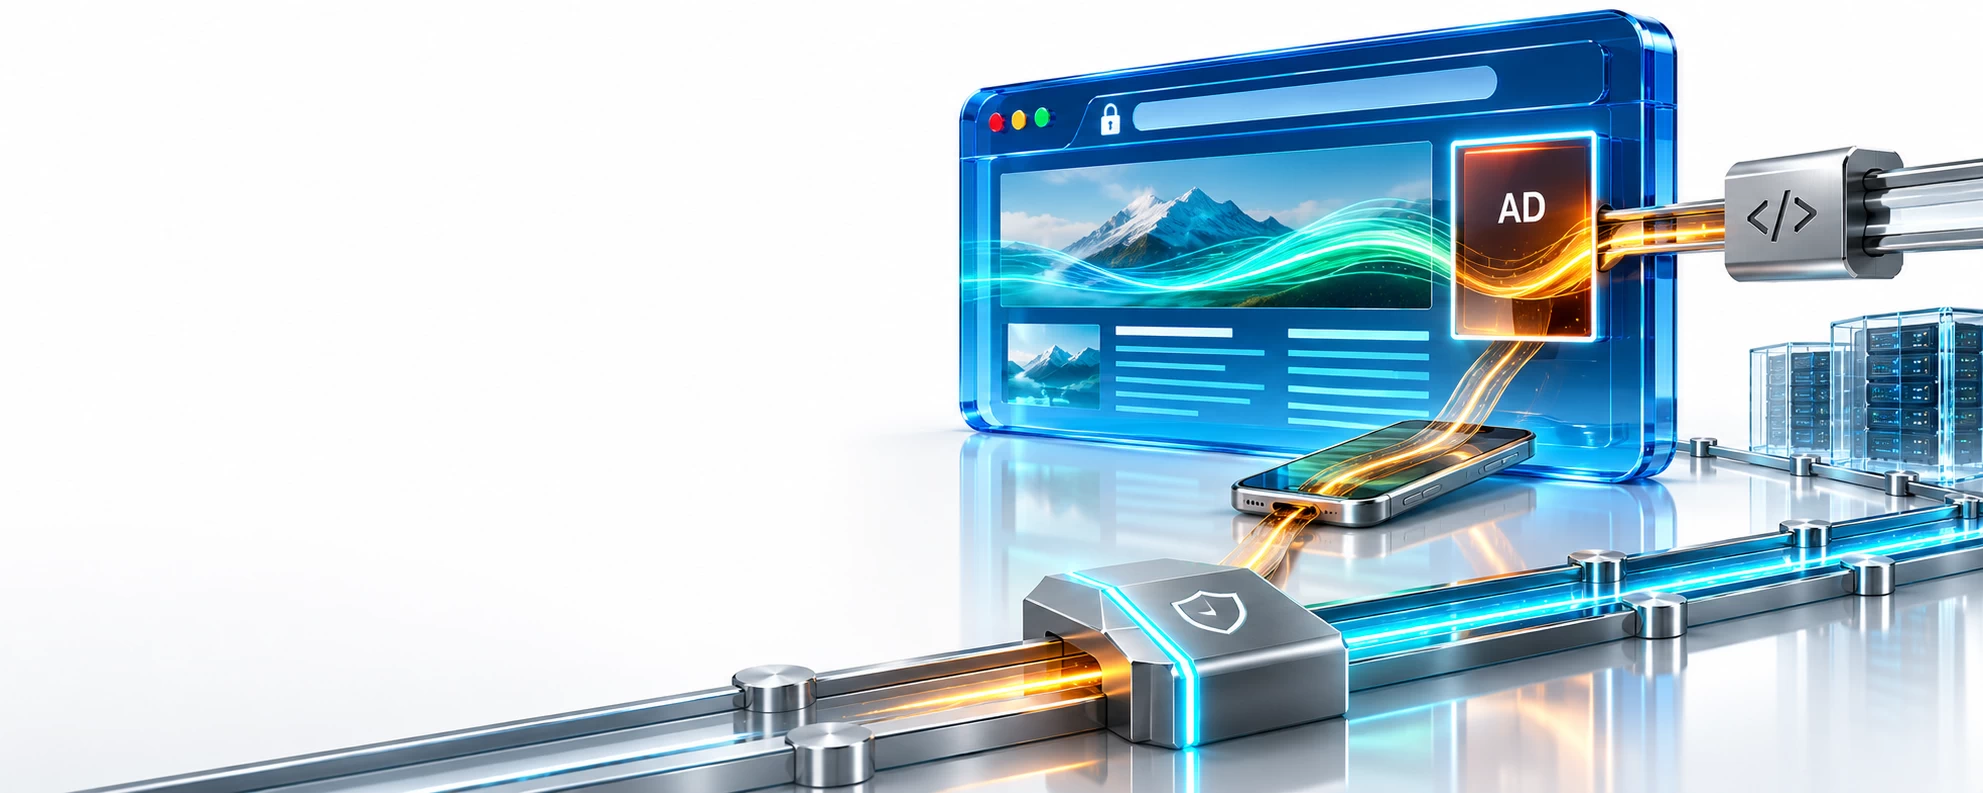
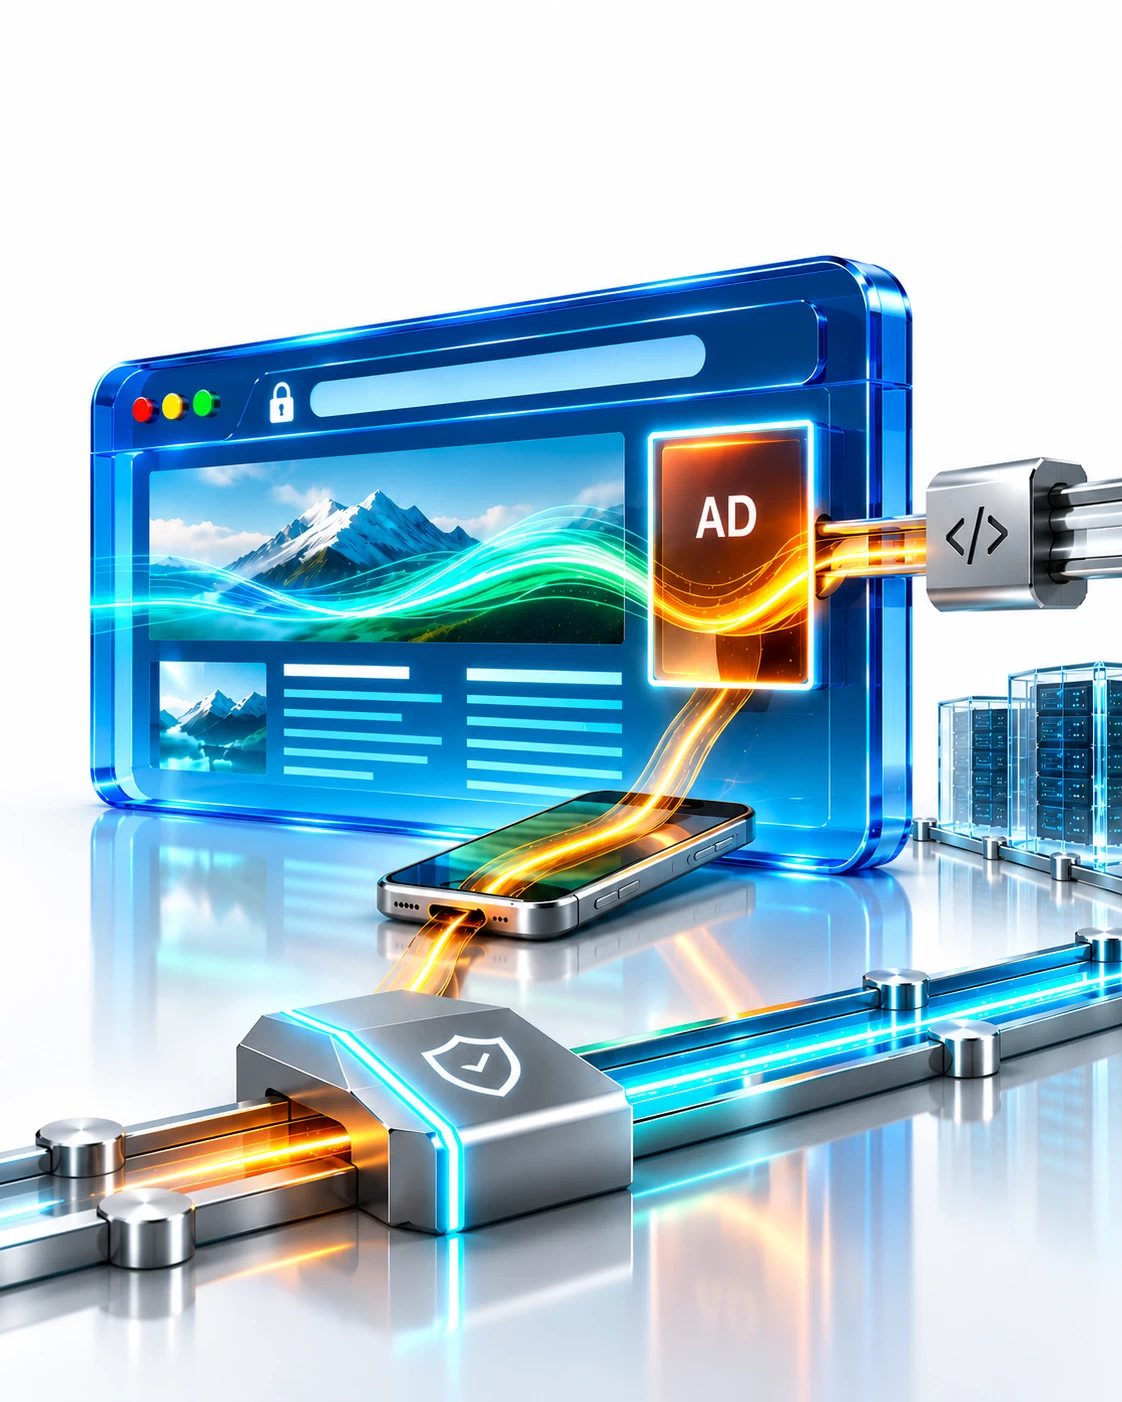
In early November, a football fan visiting VI.nl could open a match report as usual but an advertising tag shared with other publishers had been compromised. Without any click by the visitor, the ad tag could load malicious code in the same visit. VI.nl was still serving its own pages.
The business risk starts when a device used for ordinary browsing also carries work access. If an attacker obtains a password or an active session from that device, the first sign inside your organisation may be a sign-in using credentials your systems recognise. The browser event and the subsequent use of work access give your teams different opportunities to intervene.
Between 1 and 3 November 2026, an unauthorised party accessed the advertising management system and altered a tag used by VI.nl, a Dutch football publication, and other sites. GeenStijl named NextDay Media as its advertising partner. NOS reported that at least 14 Dutch websites and one Belgian site warned visitors. The code could load with the page, without an advert click.
VI confirmed that technical visitor data was sent to an attacker’s server. The data included IP addresses, pages visited, referring pages, screen dimensions, language settings and operating-system details. The recovered code also attempted to exploit certain unpatched iPhones. Individual device takeovers and theft of private data from those devices remain unconfirmed.
VI said the malicious code was removed, unauthorised accounts were removed and existing access sessions were ended. The flaw in the advertising management system was fixed on 11 November. Investigators were still assessing a further unauthorised change on that date.
Why it matters
Removing the code stopped further delivery through that configuration. The next task was to establish which visits fell within the exposure window and whether the code reached vulnerable devices. A publisher needs those facts to inform readers. An employer needs them to decide which work accounts and sessions require investigation or restriction.
Sources and further reading:
VI - Belangrijke beveiligingswaarschuwing voor bezoekers van VI.nl
https://www.vi.nl/nieuws/belangrijke-beveiligingswaarschuwing-voor-bezoekers-van-vi-nl
GeenStijl - Belangrijke veiligheidswaarschuwing bezoekers geenstijl.nl
https://www.geenstijl.nl/5193093/belangrijke-veiligheidwaarschuwing-bezoekers-geenstijlnl
NOS - Meerdere Nederlandse sites verspreidden malware via advertenties
https://nos.nl/artikel/2639562-meerdere-nederlandse-sites-verspreidden-malware-via-advertenties
The compromised tag was an instruction the publisher’s page already used to load third-party code. VI confirmed that the code sent technical information about visits to an attacker’s server. Details such as the operating system and screen dimensions let an attacker profile a device. Technical data could also be collected from computers, Android phones and iPads. The recovered exploit code targeted certain unpatched iPhones.
For a security team assessing staff exposure, the time and address of a visit are useful starting points. The script served at that time and the device’s software determine what the visitor was exposed to and whether the code could target that phone.
An employee who uses the same phone for work and personal use may still be signed in to company email and business apps while browsing the internet. At VI.nl, the malicious code sent details of visits and devices to the attacker. That was reconnaissance in the browser. If malicious code also succeeds in compromising a phone, the work credentials and active sessions it carries may be exposed.
iVerify reported a separate case in which a malicious Instagram advert infected an employee’s iPhone. The employer’s security team rotated the credentials before they could be used to access the corporate network. Had the credentials remained valid, the attacker could have tried them against company services. If the stolen credentials included an administrator account, the attacker could have used it to reach a server and start looking for other systems and data accessible from there. At that point, the reconnaissance would be taking place inside the company’s environment.
A credible mobile security alert or suspicious activity on a work account gives your team a reason to investigate. Establish which accounts and sessions were active on the phone and look for signs that someone has used them. That helps your team decide which credentials to reset and which sessions to revoke. If the attacker has already reached a protected server with stolen administrator credentials, our Server Intrusion Protection detects reconnaissance and interrupts supported malicious activity on that path.
For more on what attackers look for once they gain access, read The Attacker Had a Map Before Leadership Had a Picture.
iVerify and Report URI traced DeadTag through expired domains still referenced by old advertising and analytics tags. Thousands of websites continued to load those tags after the domains changed hands. The researchers estimated that the sites in their study received 135 million visits a month. That figure measures site traffic. Delivery depended on the device and the conditions of each visit.
In separate research, Zimperium identified 608 domains delivering Coruna-family code through October 2026. Citizen Lab documented a different use of advertising, linking targeted adverts to Candiru infections at Al Jazeera. The Instagram infection reported by iVerify was also separate from DeadTag. The practical implication for your web team is to remove old tags when a supplier relationship ends. A tag can keep calling out after everyone has stopped using the service.
Sources and further reading:
Citizen Lab - Exposing AdFection: How Discover-Tech Turned Targeted Ads Into a Pipeline for Zero-Click Mercenary Spyware
https://citizenlab.ca/research/how-discover-tech-turned-targeted-ads-into-a-pipeline-for-spyware/
iVerify - Dead Domains, Live Exploits: How Infected Ads and Expired Analytics Tags Deliver Coruna and DarkSword to iPhones
https://www.iverify.com/blog/malvertising-coruna-darksword-iphone-exploits
Google - Coruna: The Mysterious Journey of a Powerful iOS Exploit Kit
https://cloud.google.com/blog/topics/threat-intelligence/coruna-powerful-ios-exploit-kit
Zimperium - Inside Coruna and DarkSword Chains: From Web Lures to iOS Exploitation
https://zimperium.com/blog/inside-coruna-and-darksword-chains-from-web-lures-to-ios-exploitation
The employer in the iVerify case withdrew the credentials in time. If an attacker has already used compromised administrator credentials to reach a protected server, our platform can intervene there. Where deployed, Server Intrusion Protection detects reconnaissance and interrupts malicious activity, including lateral movement and data theft.
On 29 October, in a separate supplier compromise, Polymarket’s monitoring script was replaced at its usual address. The site’s browser policy still permitted the supplier’s domain. The new code used Polymarket’s trading functions to take funds from logged-in users. The company temporarily paused international trading.
For a customer portal, that creates a concrete decision. Work out which sessions could have loaded the changed code and whether the script can be removed while the service stays available.
Report URI compared archived browser policy with captures of the monitoring script. The records showed what the browser had been allowed to load and that the script served from the approved address had changed. The analysis also followed transfers on the blockchain and put the value of the theft at approximately US$2.6 million.
A clean check after the script was removed would show what a browser received at that later moment. The earlier captures let investigators compare the two versions. Retain dated copies of the scripts your team observes so it can make that comparison after an incident.
Sources and further reading:
Report URI - Polymarket's CSP Allowed Every Part of the $2.6 Million Crypto Theft
https://report-uri.ghost.io/polymarkets-csp-allowed-every-part-of-the-2-6-million-crypto-theft/
Associated Press - Polymarket paused international trading after a security issue involving a third-party provider
https://apnews.com/article/polymarket-pause-trading-prediction-markets-cd33bc1f9bf623103e1aeef3897846b5
Reuters - Polymarket resumes trading after third-party security breach, to reimburse users
https://www.reuters.com/business/polymarket-reports-major-outage-suspends-trading-actions-2026-10-29/
Establish what ran
An inventory of approved scripts tells you where to look. Dated copies of what those addresses served, browser records where available, and visit logs help your team work out which customers may have received the changed code. Give the service owner a way to remove the affected script and verify from a browser when it stopped loading. That narrows the investigation and gives the communications team a defensible exposure window.
Withdraw access carried by the device
An exposed device may still be signed in to work. Have the identity team identify affected accounts and sessions, rotate exposed credentials and revoke active access where the facts justify it. That closes the routes the device already carried while the investigation establishes what else was exposed.
Interrupt activity on protected servers
If an administrator’s credentials had been stolen, the investigation has moved inside your environment. Server Intrusion Protection interrupts supported malicious activity on protected paths. Stopping reconnaissance and lateral movement there limits the number of systems, data stores and backups your teams have to investigate and recover.
At VI.nl, the incident could begin with a visitor opening a match report. If the activity ends at the browser, the immediate work is to establish exposure and decide who needs to be informed. If stolen credentials are later used on a protected server, automatic containment interrupts the malicious activity it detects there while your team works back to the original device. That intervention protects the systems and data the attacker was trying to reach next.
Explore the assumptions behind your existing controls in Cybersecurity Blind Spots.
To test containment at the point where ransomware starts encrypting files, ask about our Resilience Assessment. The controlled comparison runs with your existing security controls active, first without and then with Ransomware Containment enabled.
In “The Organisation Itself Becomes The Bottleneck”, we follow a containment recommendation from your security team to the people who can approve it. The article asks which restrictions your responders can apply immediately and who decides when the action would interrupt an essential service.
Wednesday 18 Nov 2026, Leadership-series #11: "The Organisation Itself Becomes The Bottleneck"
Friday 20 Nov 2026, Operational Attack-series #11: "The Extortion Trap Begins Before the Ransom Note"
Monday 23 Nov 2026, Resilience-series #12: "When Ransomware Becomes a Life-Critical Decision"