Article #27 (extra edition)
Published: 30 October 2026
By Stan van Gemert | S10 Group
By Stan van Gemert
When attacks move series
The previous publication, "When the System That Defines Trust Can No Longer Be Trusted", examined what happens when an account, token or administrative path still looks legitimate even though the authority behind it has become unsafe.
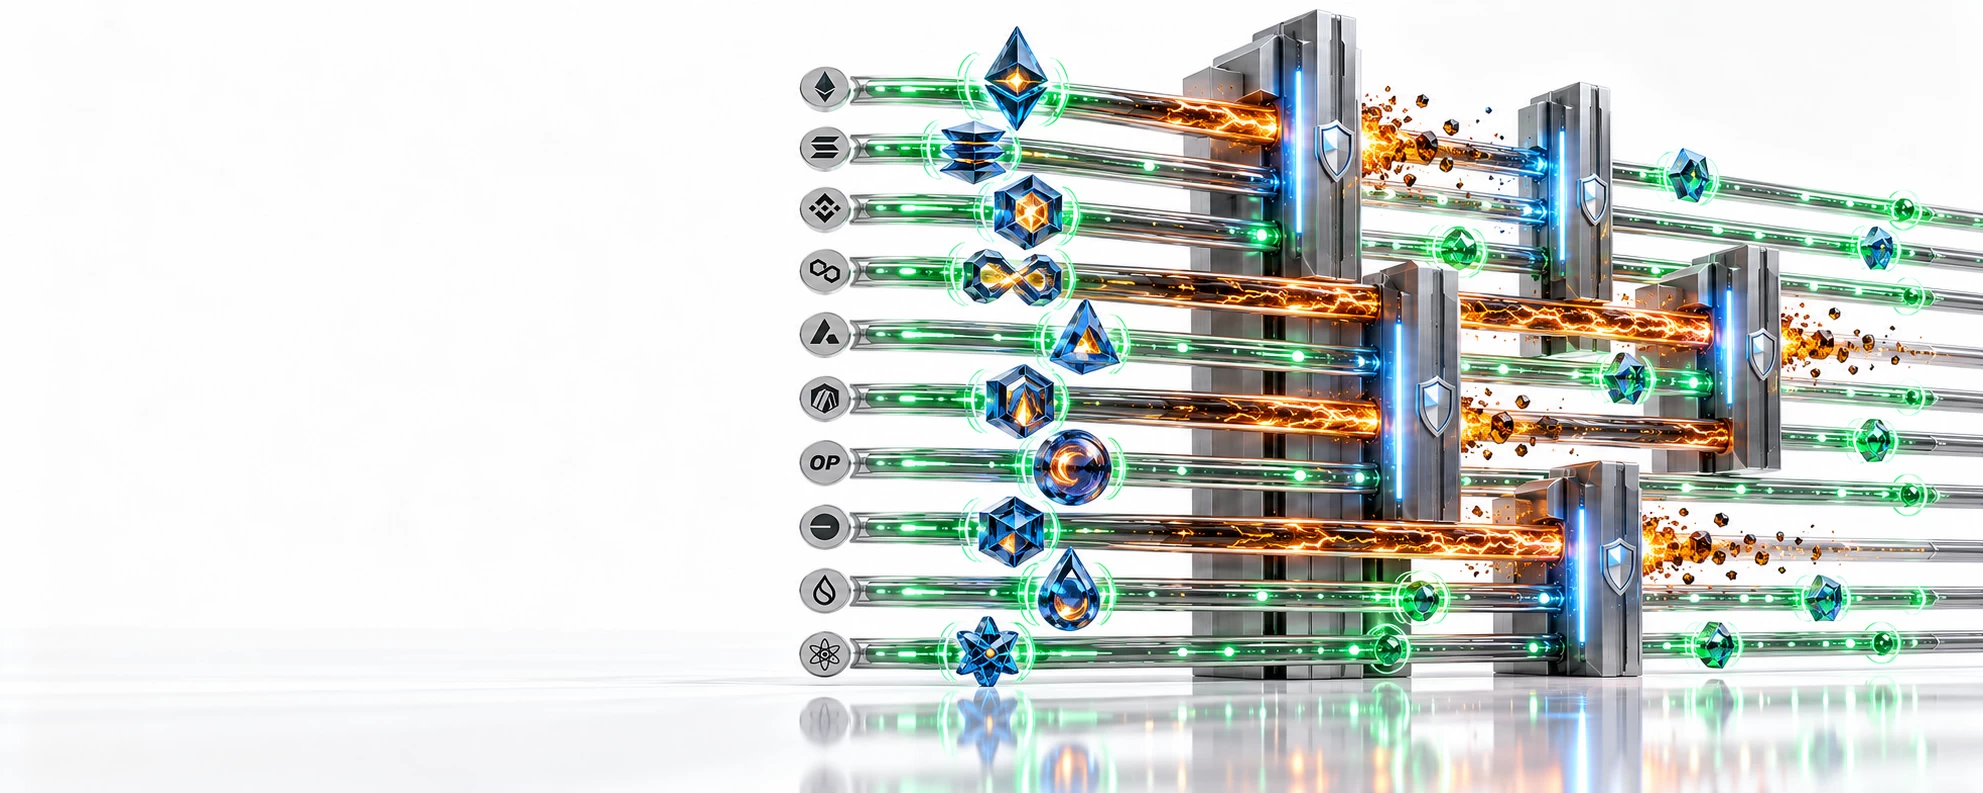
This new special carries that problem into the 29 October 2026 Binance incident. Binance estimated an impact of about USD 6.3 billion, while TRM Labs traced approximately USD 6.36 billion across ten blockchains, with most of the value moving in about twenty minutes. The networks processed recognised signatures and delegated authority, yet the economic instruction was unauthorised.
The next publication, "When Every Minute Matters, Readiness Cannot Wait", moves from valid-looking instructions to the shrinking response window. It asks what must already be prepared when a narrow intervention is available now but delay will make every later option broader, slower and more disruptive.
Binance’s 30 October security update estimated the total impact at around USD 6.3 billion. Its initial investigation suggested that a compromised DevOps engineer’s laptop may have enabled access to a service container and the submission of unauthorised withdrawal transactions. The company said it had found no indication that wallet private keys were leaked and would publish a full technical post-mortem after completing the investigation.
The provisional language matters. A possible entry point is not yet a complete account of how access moved from an endpoint into systems able to instruct high-value transfers across several networks. Subsequent company reporting referred to multiple factors and an investigation into the full attack path. Assigning a definitive root cause, a single failed control or individual responsibility would therefore go beyond the available account.
Binance temporarily suspended withdrawals, revoked affected authorisation, engaged law enforcement and blockchain-intelligence partners and said it would cover losses through its SAFU fund and company resources. Those actions describe response and remediation. They do not complete the forensic explanation of how transaction authority was obtained or exercised.
Binance provides a preliminary company account: a possible compromise of a DevOps laptop, access to a service container, unauthorised withdrawals and no identified private-key leak. TRM provides a separate on-chain analysis of transfer timing, mechanisms, asset movement and attacker attribution.
Together, the sources support the conclusion that recognised technical authority was used to execute transfers the business did not authorise. They do not yet provide one complete, settled reconstruction of the internal compromise.
Sources:
Associated Press - Binance flags ‘potential security issue,’ says approximately USD 6.3 billion impacted
https://apnews.com/article/binance-cryptocurrency-security-39cda8ceb8095e036334a18549d3d20d
TRM Labs - North Korea Steals USD 6.36 Billion From Binance in the Largest Hack in History
https://www.trmlabs.com/resources/blog/north-korea-steals-usd-6-36-billion-from-binance-in-the-largest-hack-in-history
Ethereum - EIP-7702 Set Code for EOAs
https://eips.ethereum.org/EIPS/eip-7702
Note: The Binance account remains preliminary. TRM’s attribution and on-chain reconstruction are analytic findings, not a substitute for Binance’s final technical post-mortem.
Distributing assets across several blockchains, wallets or applications can reduce some forms of concentration. It does not automatically separate the operational authority used to instruct them.
Ten transaction rails may each validate a signature correctly. If several of them depend on an upstream signing service, privileged workflow or approval process that an attacker can influence, each rail may honour the resulting instruction. Transaction checks have worked at protocol level while the shared business-authority boundary has failed.
TRM’s observation of Ethereum delegation alongside separately signed transfers makes that architectural risk credible. It does not prove that one shared signer caused every movement. The full route from initial access to authorised-looking transfers remains under investigation.
The lesson travels beyond cryptocurrency. Treasury APIs, payment gateways, privileged service accounts, supplier interfaces and automated settlement processes all translate recognised authority into consequential action. Their technologies differ, but the control question is similar: when the account or service exercising that authority becomes unsafe, can the business reject the instruction before execution makes the outcome difficult or impossible to reverse?
Prevention, revocation, suspension, freezing and recovery are separate controls. Blocking an instruction before execution protects value in a different way from freezing assets after receipt, and a frozen asset has not necessarily been returned to its owner.
The public figures illustrate the distinction. Binance reported about USD 3 billion frozen on-chain; TRM counted about USD 2.7 billion at an earlier snapshot and within its own methodology. Both are time-bound accounts of restricted assets, not confirmed recovery totals.
Sources:
Associated Press - Binance flags ‘potential security issue,’ says approximately USD 6.3 billion impacted
https://apnews.com/article/binance-cryptocurrency-security-39cda8ceb8095e036334a18549d3d20d
TRM Labs - On-chain tracing and freeze snapshot
https://www.trmlabs.com/resources/blog/north-korea-steals-usd-6-36-billion-from-binance-in-the-largest-hack-in-history
Reuters - Hackers steal USD 6.3 billion from Binance in record heist blamed on North Korea
https://www.reuters.com/legal/transactional/tether-circle-freeze-238-billion-after-binance-reports-security-incident-2026-10-29/
An unavailable financial system presents an obvious operational problem. A system that continues executing instructions can be more deceptive. A transaction may settle, the ledger may reconcile and the signature may be authentic to the key or delegated authority presented. None of those facts proves that the business approved the movement of value.
Binance’s commitment to cover losses, its work to freeze assets and the restoration of services each address a different consequence. Reimbursement can protect customers financially. Service restoration can reopen operations. A post-mortem can explain the attack path. None should be used as a proxy for the others.
Conventional finance faces the same separation. Resilience is not limited to keeping the transaction engine online. It also requires instructions to be authenticated in context, authorised by the right party, restricted when authority changes and reconciled against actual business obligations.
Once settlement is complete, the available response becomes narrower. The stronger control opportunity lies before the instruction crosses the point at which execution cannot readily be undone. Separation of signing authority, transaction policies, privileged-access controls, abnormal-transfer limits, revocation capability and emergency restrictions all become material at that boundary.
No single control provides a universal answer. A rule that rejects an anomalous instruction can interrupt legitimate business. A sweeping halt may protect assets but affect customers and counterparties. Delay can preserve short-term normality while more value leaves the business’s control. Those trade-offs should not be discovered for the first time during the incident call.
The executive test is therefore not only whether a compromise can be detected. It is whether a suspicious but technically valid instruction can meet an enforceable business boundary, and whether someone already holds the authority to apply that boundary at transaction speed.
The Binance incident shows why early detection only becomes decisive when it can trigger an effective restriction before compromised authority creates irreversible consequences. Once accepted access is being abused, every additional minute gives the attacker more time to conduct reconnaissance, use legitimate routes, move assets and make recovery substantially harder.
Within the environments it protects, our platform closes that gap by detecting and containing malicious activity after entry. Earlier intervention can interrupt lateral movement, prevent further data theft, restrict malicious server activity and protect supported virtual environments before one compromised path becomes a much wider security and operational crisis.
The Binance incident is recent, and the full sequence of events has not yet been established. Even so, the information available already exposes a control question with relevance far beyond cryptocurrency.
Your organisation may never operate a crypto wallet. It may still rely on payment gateways, automated treasury processes, service accounts, cloud administration and supplier APIs that convert access into action. The issue is whether the permissions attached to those systems and connections still reflect legitimate business authority after an identity, session or service has been compromised.
When the next valid-looking instruction is no longer legitimate, what can stop it before execution turns compromised authority into irreversible loss?
"When Every Minute Matters, Readiness Cannot Wait" moves from the transaction boundary to the response window around it. A restriction that is narrow and proportionate at the first credible signal may become a broad operational decision after the attacker gains more reach, creates more dependencies or removes more options.
The next article examines the triggers, decision rights and response paths that must exist before urgency arrives, so containment can still happen while the available choice remains precise
Monday 2 Nov 2026, Resilience-series #9: "When Every Minute Matters, Readiness Cannot Wait"
Wednesday 4 Nov 2026, Leadership-series #9: "The First Hour Exposes Decision Readiness"
Friday 6 Nov 2026, Operational Attack-series #9: "The Internal Report Was Clean. The Business Still Stopped."